Learn
NEWVenvera speaks your language: the full platform, in English, German, Spanish, Bulgarian, Arabic and Chinese.See what’s new →
BLOG
Insights on EU compliance, framework deep-dives, and platform updates.
All posts
Learn
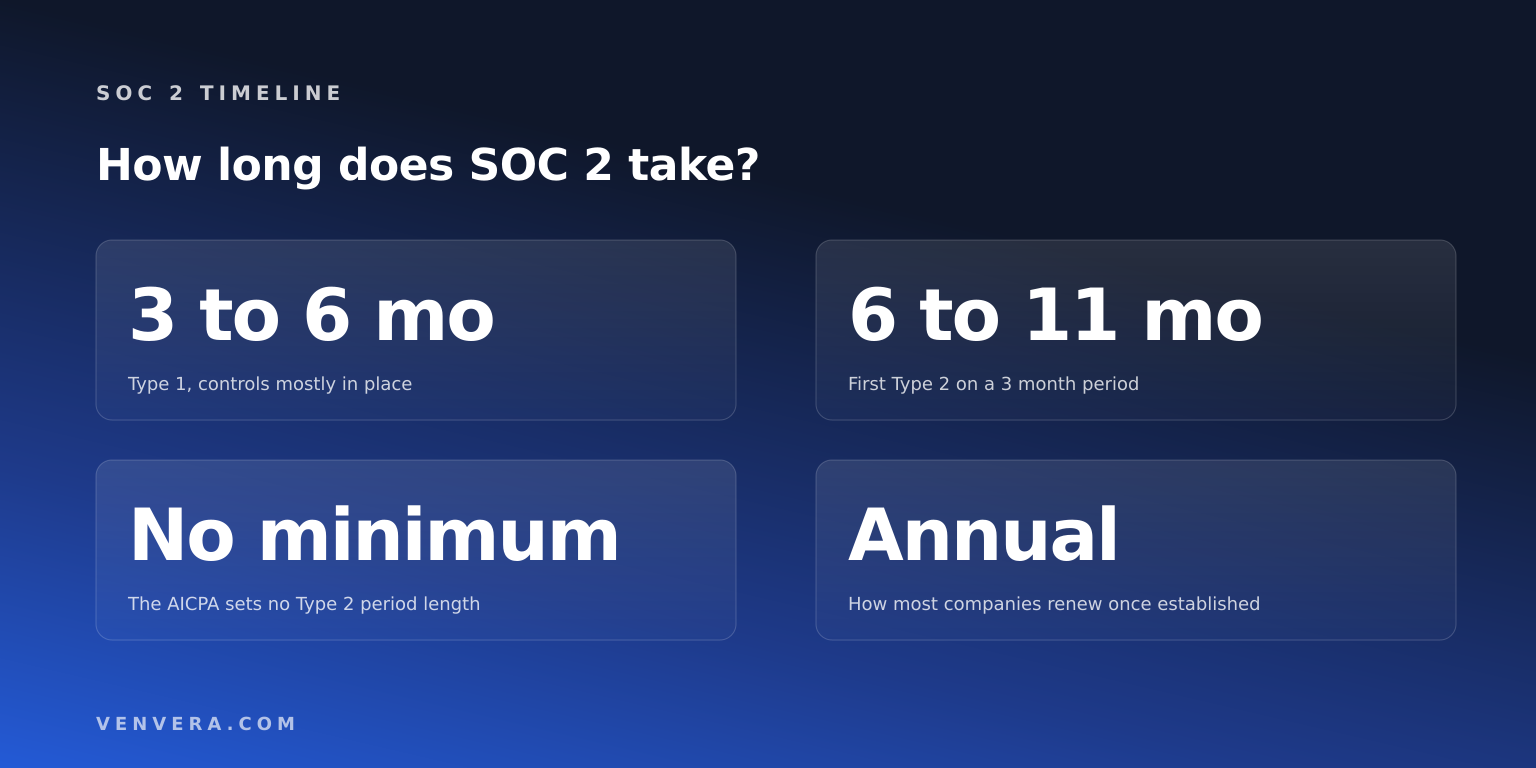
How Long Does SOC 2 Take? The Real Calendar
No AICPA rule fixes how long SOC 2 takes; the period you choose does. Each phase timed from CPA firm guidance, with the arithmetic for Type 1 and Type 2.
Learn
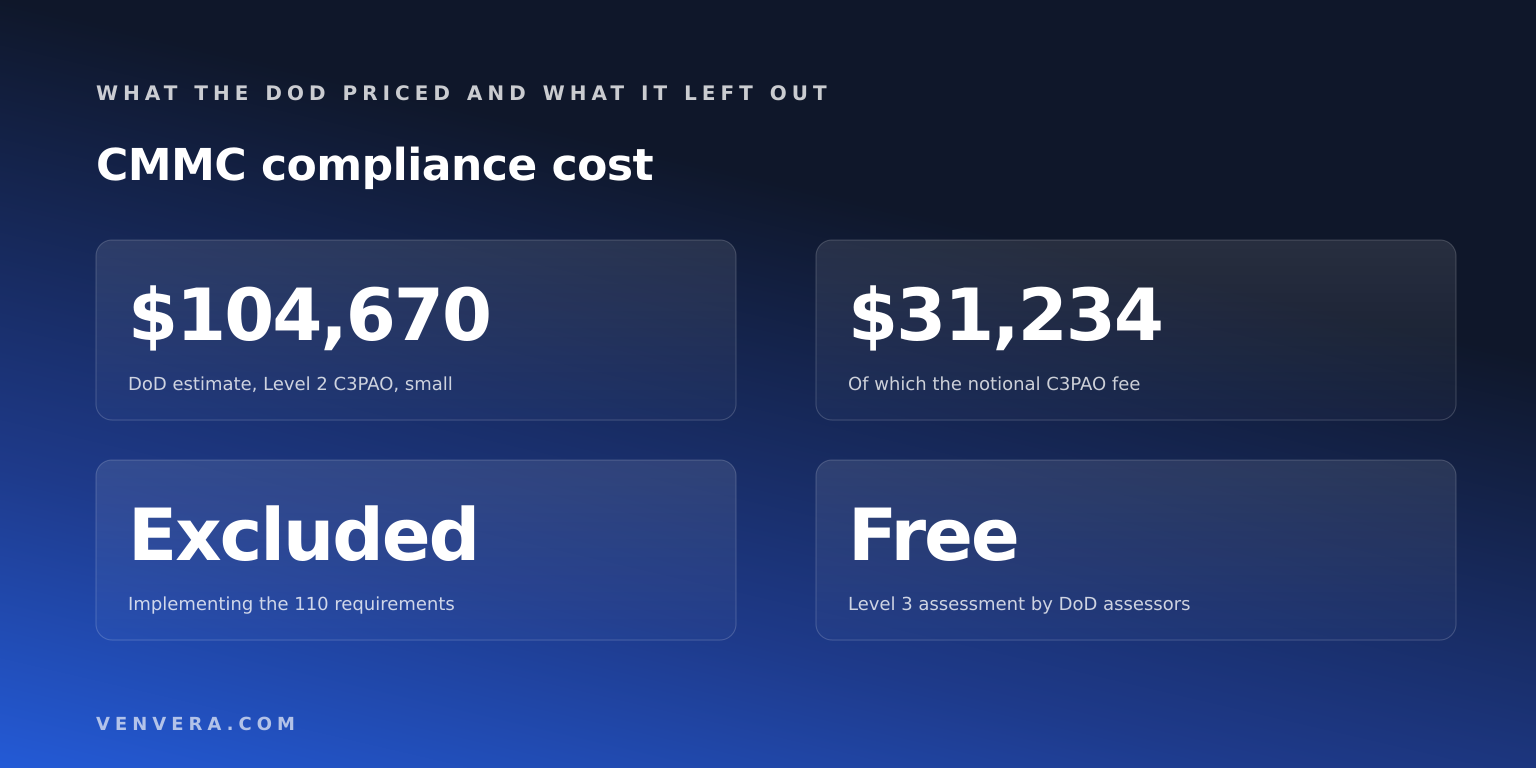
CMMC Compliance Cost: What the DoD Estimated
The DoD puts a small firm's Level 2 C3PAO route at $104,670 over three years, but that figure leaves out the controls. What it covers and what you must add.
Learn
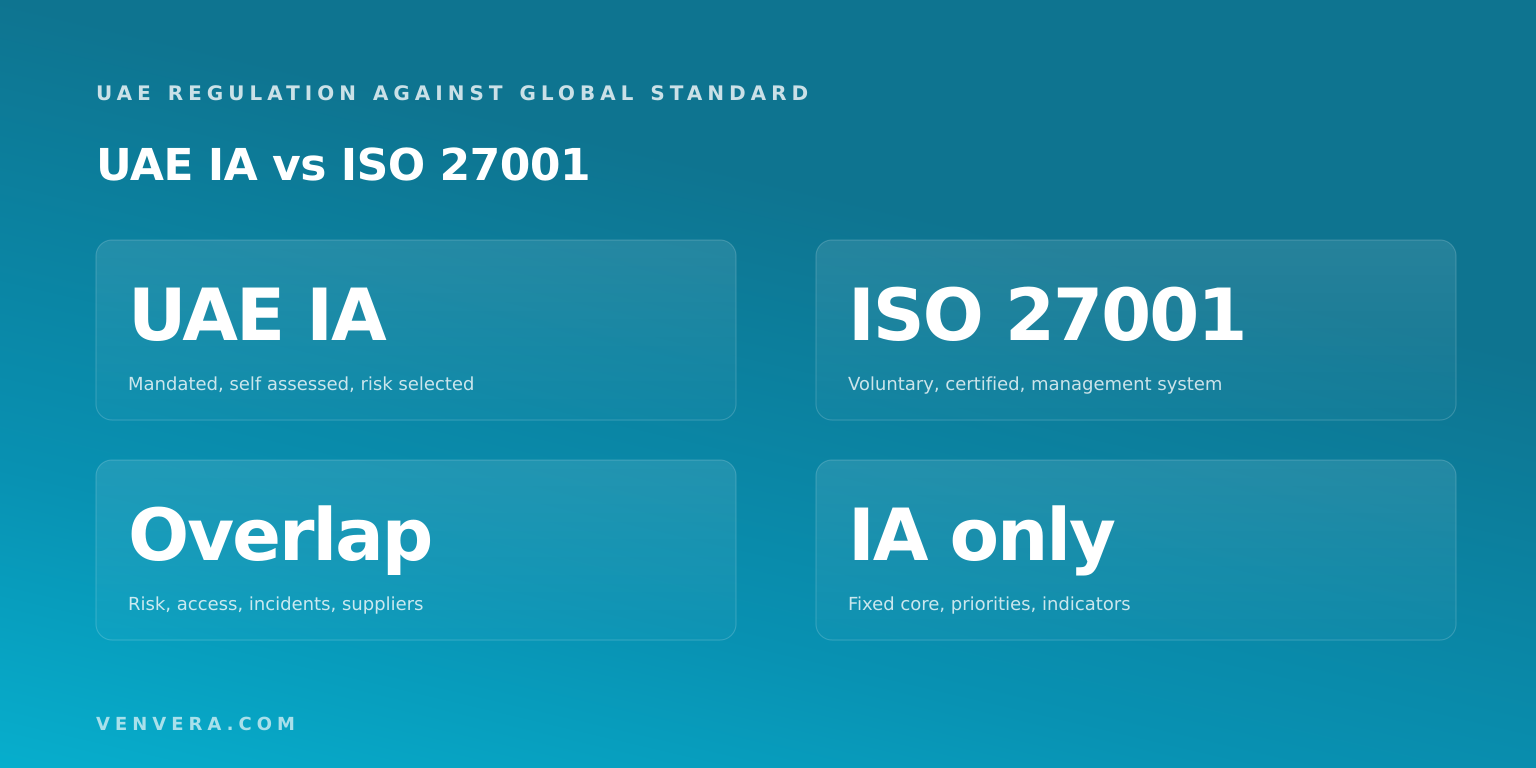
UAE IA vs ISO 27001: Where They Differ
An ISO 27001 certificate builds much of a UAE IA programme but stands in for none of it. The overlap, the IA only rules, and which edition you are held to.
Learn
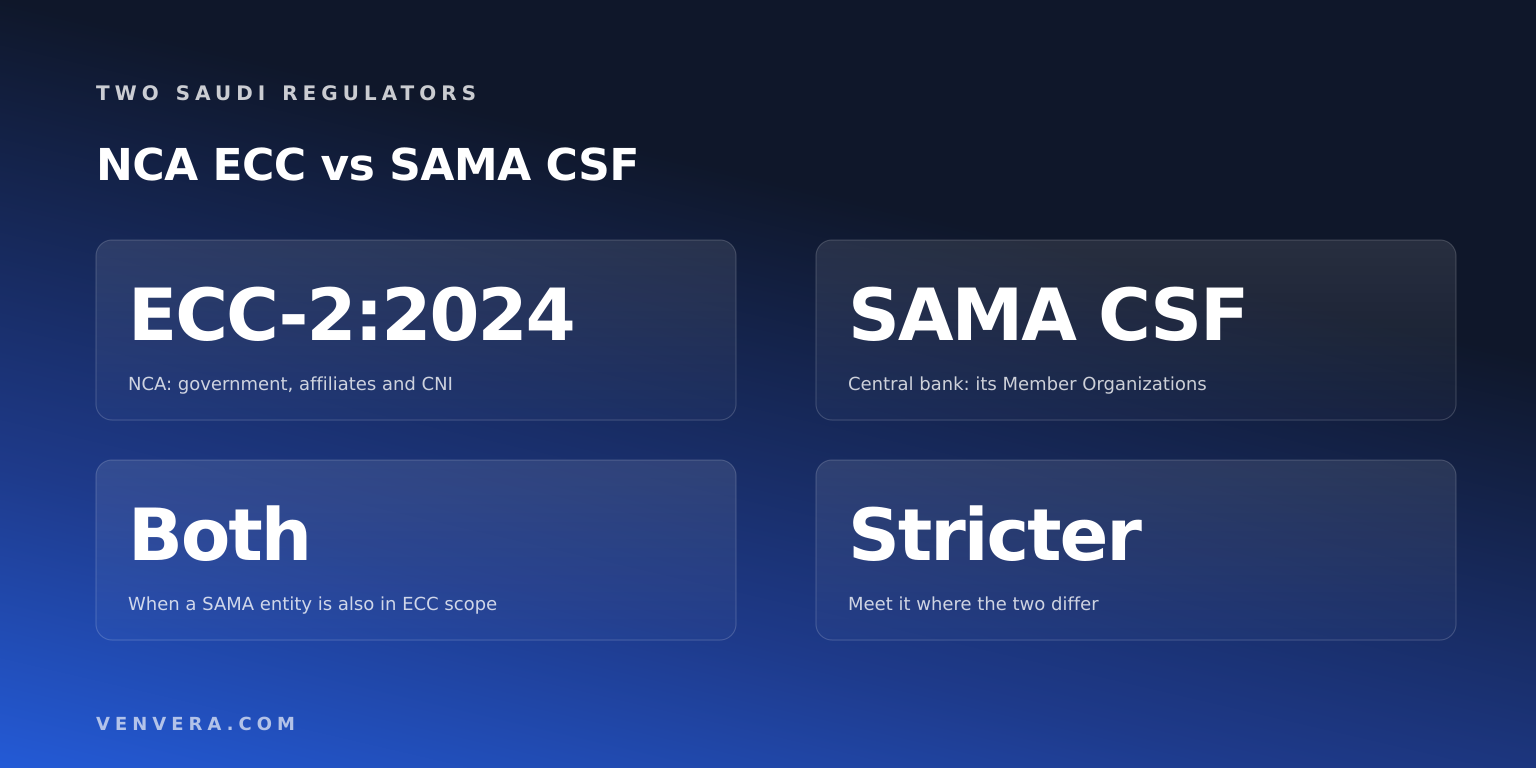
Saudi NCA ECC vs SAMA CSF: Scope and Differences
Who the NCA's ECC-2:2024 and the SAMA CSF each bind, when a financial institution answers to both, and the rules where the two disagree. From the texts.
Learn
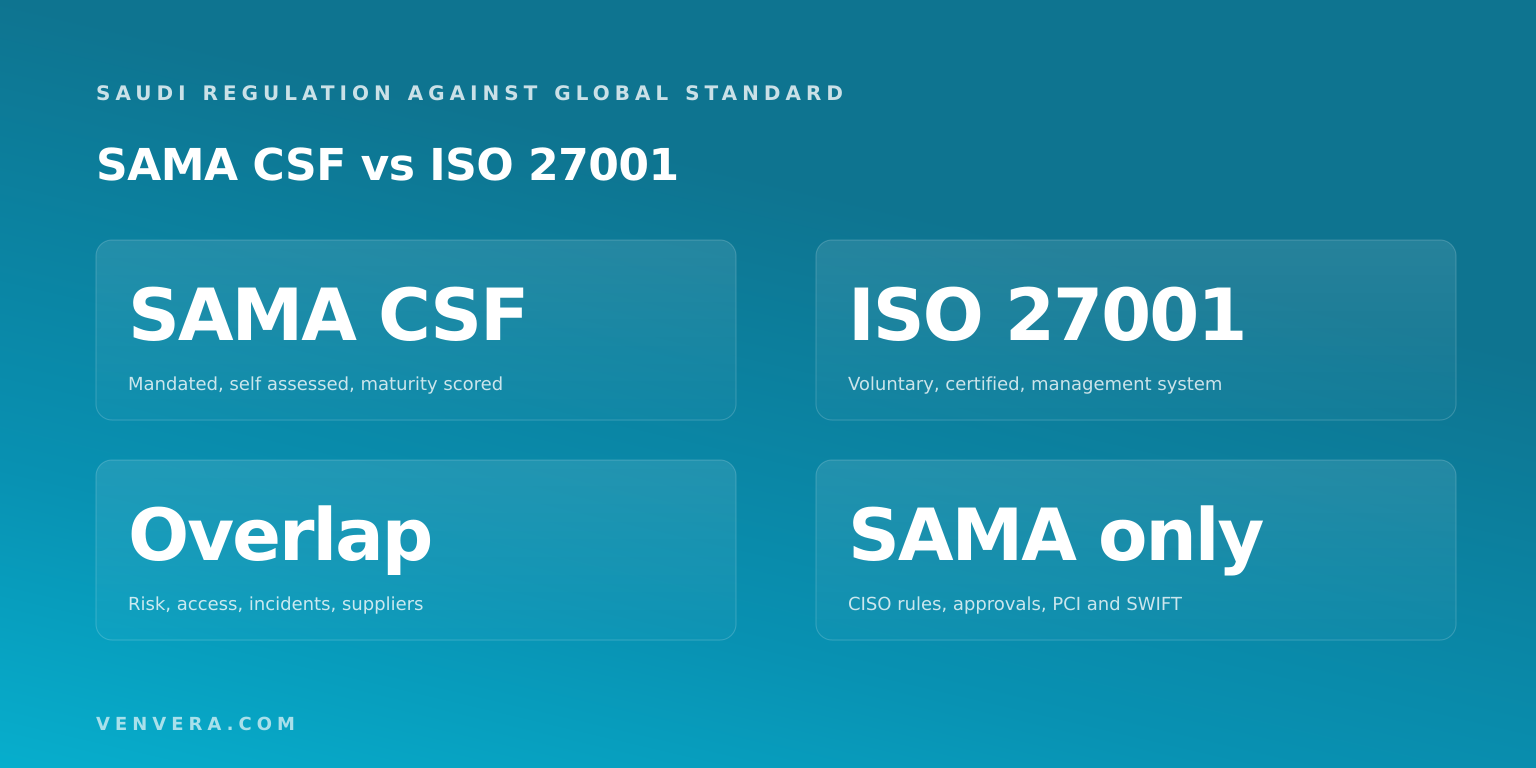
SAMA CSF vs ISO 27001: What a Certificate Covers
An ISO 27001 certificate builds much of a SAMA CSF programme but replaces none of it. Where the two overlap, and the SAMA rules the standard never asks for.
Learn
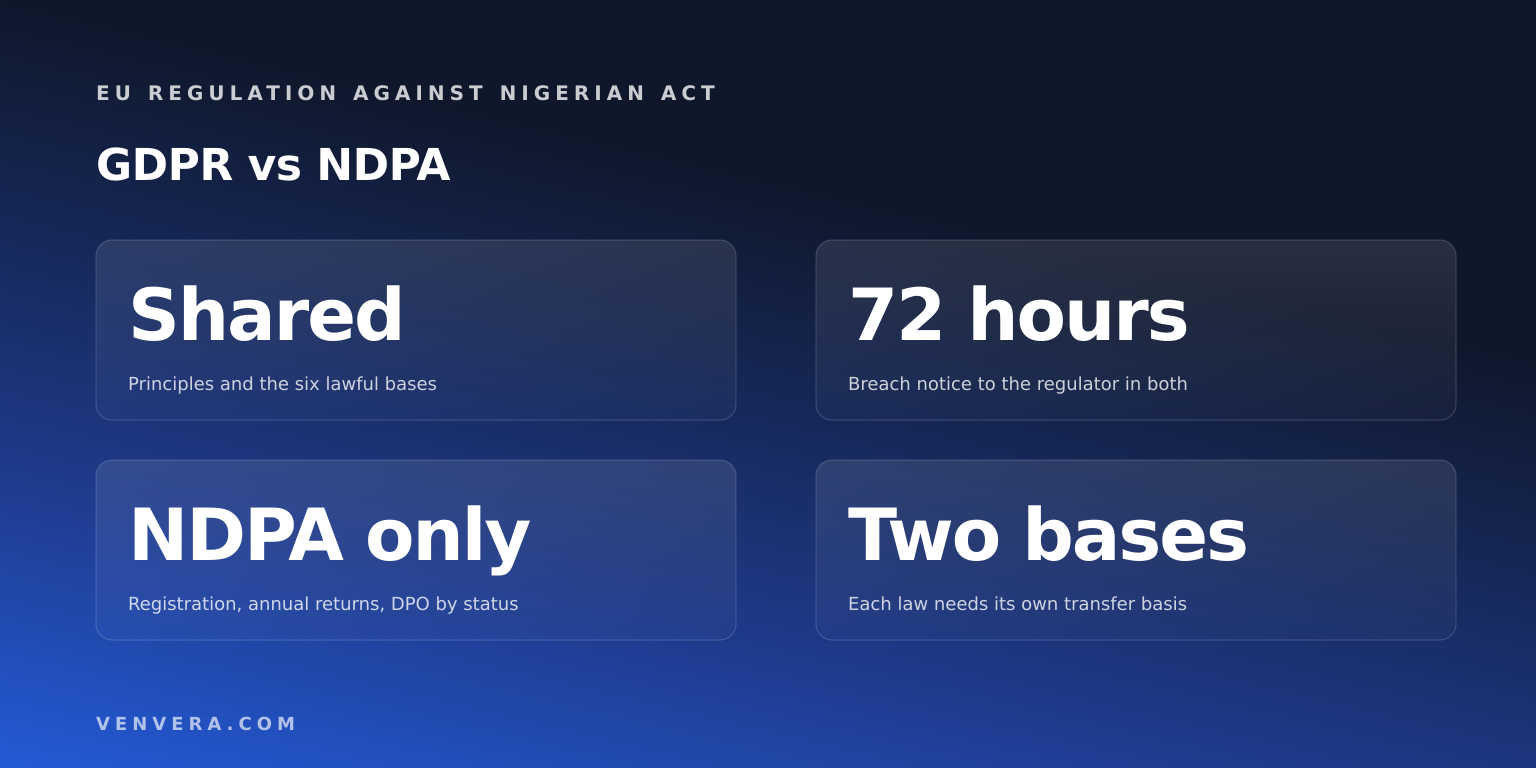
GDPR vs NDPA: Where Nigeria's Law Differs
The NDPA borrows GDPR's principles and six lawful bases, then parts ways on registration, annual returns, breach notice, fines and transfers. Side by side.
Learn
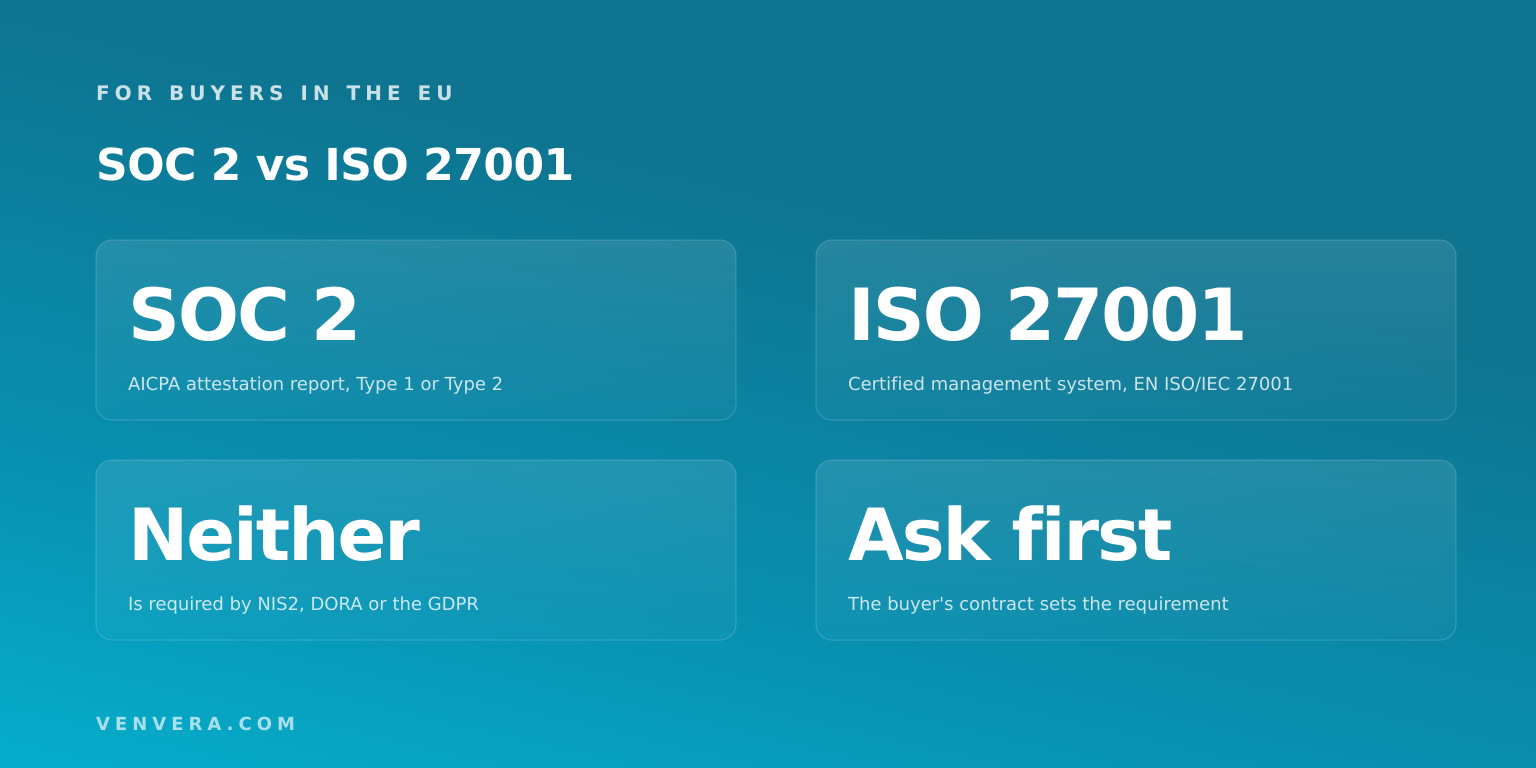
SOC 2 vs ISO 27001: What EU Buyers Ask For
NIS2, DORA and the GDPR require neither. What those laws and German C5 say about each, and how to pick the one an EU customer's procurement team will accept.
Learn
PCI DSS vs ISO 27001: Scope, Proof and Overlap
PCI DSS protects card data under rules the brands enforce; ISO 27001 certifies a system you scope. Where they overlap, and why neither replaces the other.
Learn
ISO 27001 vs DORA: What the Certificate Covers
DORA never mentions ISO 27001. Where an ISMS already answers its ICT risk articles, and the reporting, register, contract and testing duties it leaves open.
Learn
SOC 2 Audit: What to Expect From Start to Report
What happens in a SOC 2 examination: the description and assertion you write, how a Type 2 is tested, vendors, the four possible opinions, the final letter.
Learn
HIPAA Fines and Penalties: What OCR Really Charges
HIPAA penalty tiers at the amounts in force since January 2026, the 2019 yearly caps OCR still applies, how one gap becomes a daily violation, real cases.
Learn
PCI DSS Compliance Cost: What Drives the Bill
Nobody publishes a PCI DSS price. What sets yours: the validation route your card brand and acquirer require, the tests the standard mandates, and your scope.
Learn
ISO 27001 Audit: What to Expect in the Room
What happens inside an ISO 27001 certification audit: the opening meeting, sampling and interviews, major and minor findings, the closing meeting, the report.
Learn
How Long Does ISO 27001 Certification Take?
No standard sets a duration. What has to exist before stage 1, what happens between the two audit stages, and what can hold the certificate back.
Learn
GDPR Fines and Penalties: What Changed in 2026
The two GDPR fine tiers, whose turnover counts, why fault is now required, how the EDPB sets the amount, and the fines and rule changes of 2026.
Learn
SOC 2 Cost for Companies Outside the US
What sets a SOC 2 fee when you are not a US company: who may sign the report, AICPA versus ISAE 3000, report type, the period and the scope.
Learn
ISO 27001 Certification Cost: What Sets the Price
There is no ISO price list. How audit days follow headcount, what the three year cycle bills you for, and what accreditation in Europe changes.
Learn
NIS2 for Healthcare Providers: Scope and Duties
Which hospitals, clinics and pharmacies NIS2 covers, why a public hospital is sized like any other, and what Articles 20, 21 and 23 ask of them.
Learn
DORA for Payment Institutions: Scope and TLPT
Which payment and e-money institutions DORA covers, what it changed in PSD2 incident reporting, and when a payment firm must run TLPT.
Learn
NIS2 for Manufacturers: Scope and Obligations
Which manufacturers NIS2 covers, why most are important rather than essential entities, and what Articles 20, 21 and 23 ask of a plant operator.
Learn
DORA for Insurers: Scope, Solvency II and TLPT
Which insurers, reinsurers and intermediaries DORA covers, what it changed in Solvency II, and when an insurer must report an incident or run TLPT.
Learn
MiCA Requirements for CASPs Explained
What MiCA Title V asks of a crypto-asset service provider: authorisation, capital, governance, client asset safekeeping and the service rules.
Learn
EU AI Act High-Risk Requirements Explained
The seven requirements a high-risk AI system must meet under Articles 8 to 15, what providers and deployers each owe, and what the 2026 Omnibus changed.
Learn
UAE IA Audit: What to Expect
How UAE IA compliance is checked: self-assessment reports via your sector regulator, audits and tests where TRA sees fit, and the evidence it reads.
Learn
eIDAS 2.0 Relying Party Requirements
What eIDAS 2.0 asks of a wallet relying party: register, request only registered data, identify yourself, validate, accept pseudonyms, keep other routes.
Learn
SAMA CSF Audit: What to Expect
A SAMA CSF audit tests your periodic self-assessment: evidence per subdomain, maturity level 3 as the floor, independent audits and waivers for real gaps.
Learn
Solvency II Governance Requirements in Detail
Solvency II governance in Articles 258 to 275 of Delegated Regulation 2015/35: the 12 general duties, key function tasks, outsourcing clauses and pay rules.
Learn
Cyber Resilience Act Requirements Explained
The CRA requirements in one place: the 13 product properties and 8 vulnerability duties in Annex I, the Article 13 duties, and Article 14 reporting.
Learn
HIPAA Risk Assessment: What OCR Actually Checks
The HIPAA risk analysis from the regulation itself: two Required duties, the nine elements OCR expects, a scored example, and what a missing one has cost.
Learn
Nigeria NDPA Compliance Cost
Registration is N10,000 to N250,000 and audit returns N100,000 to N1,000,000 a year under the 2025 GAID. The fees, the six budget lines, and what recurs.
Learn
DORA Requirements Explained
DORA sets five sets of requirements: ICT risk management, incident reporting, resilience testing, third-party risk and information sharing. What each asks.
Features
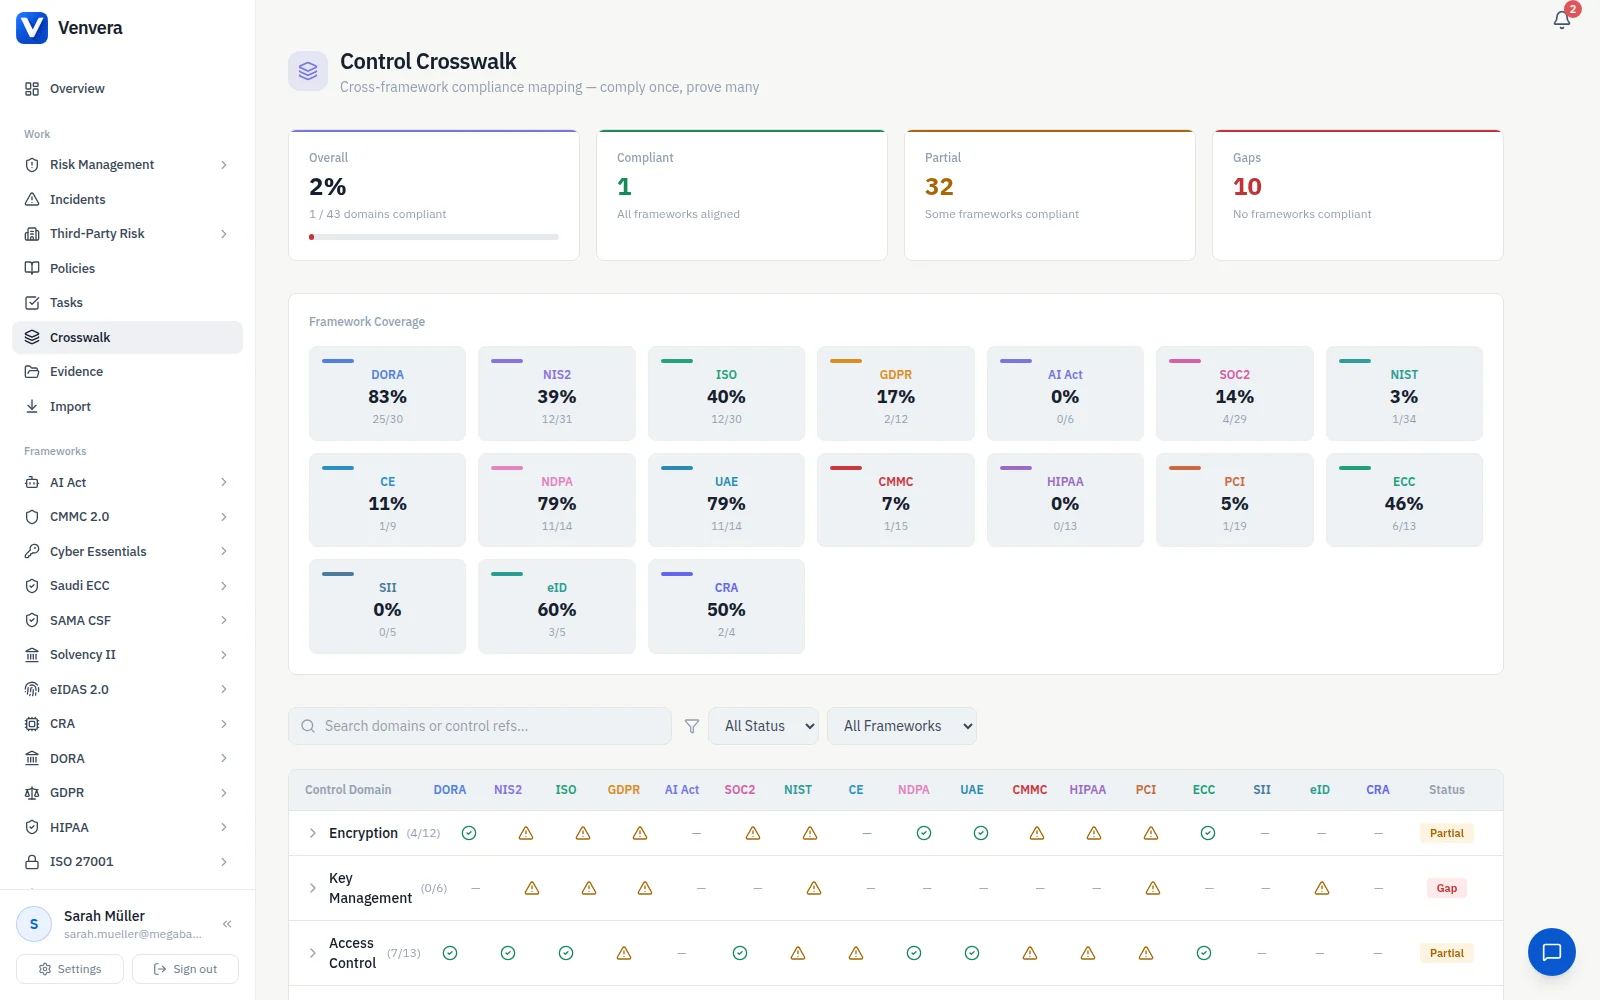
How Venvera Runs Multi-Jurisdictional Compliance
One control set across twenty frameworks, separate evidence per legal entity, and the artefact each regulator asks for, in its own template and language.

Learn
Solvency II Pillar 2 Compliance Cost
The Commission's own impact assessment prices Solvency II at EUR 12m one-off and EUR 2.7m a year on average. What that means for a Pillar 2 governance budget.

Learn
NIS2 Article 21 Requirements Explained
Article 21 of NIS2 requires ten minimum cybersecurity measures on an all-hazards basis, sized by exposure, size and impact. What each point asks for.

Best
Best Enterprise Risk Management Software (2026)
Fourteen enterprise risk management platforms sorted into four segments, a weighted scorecard, three-year cost, a 90-day plan and fifteen RFP questions.

Learn
Who Needs FedRAMP? The 2026 Scope Test
The three conditions that put a cloud service in FedRAMP scope, the six exclusions, the four classes and which you can enter today, and what it costs.

Learn
Risk Management Frameworks: Which One, and How
Ten risk management frameworks compared on what they produce and who accepts it, with a decision tree, a 90-day plan and the regulation each one satisfies.

Learn
What Is Solvency II? The Three Pillars Explained
Solvency II is the EU prudential regime for insurers in Directive 2009/138/EC. The three pillars, who is in scope, and what changes on 30 January 2027.

Learn
Solvency II ORSA Review: What to Expect
A Solvency II ORSA review tests Article 45 as a process: a board approved policy, a record of each run, real challenge, and a report filed within two weeks.

Best
Vendor Risk Management as a Service (2026)
Vendor risk management as a service, also sold as TPRM as a service: what it includes, the four delivery models, cost, and what you cannot outsource.

Best
Multi-Jurisdictional Compliance Software (2026)
Multi-jurisdictional compliance software: what it must do for companies regulated in several countries, where single-country tools break, and a score table.

Learn
Saudi NCA ECC Compliance Cost: What Drives It
There is no price list for ECC-2:2024. What the 108 controls make you pay for, the four lines that are hires and audits, not software, and how to size yours.

Learn
EU AI Act Compliance Timeline: How Long It Takes
How long does EU AI Act compliance take? Weeks for most deployers, 9 to 18 months for a high risk provider. The phases and the date to plan against.

Best
Third-Party Risk Management Solutions: 2026 Guide
Third party risk management solutions for regulated companies: four kinds of platform, what DORA, NIS2 and ISO 27001 require, and a scoring table to choose.

Learn
eIDAS 2.0 Fines and Penalties Explained
eIDAS 2.0 fines for trust service providers reach at least EUR 5 million or 1% of turnover. What Article 16 fixes, and what relying parties actually risk.

Learn
Nigeria NDPA Requirements Explained
What the Nigeria Data Protection Act 2023 and the 2025 GAID require, section by section, and the 200 data subject line that doubles the list.
Learn
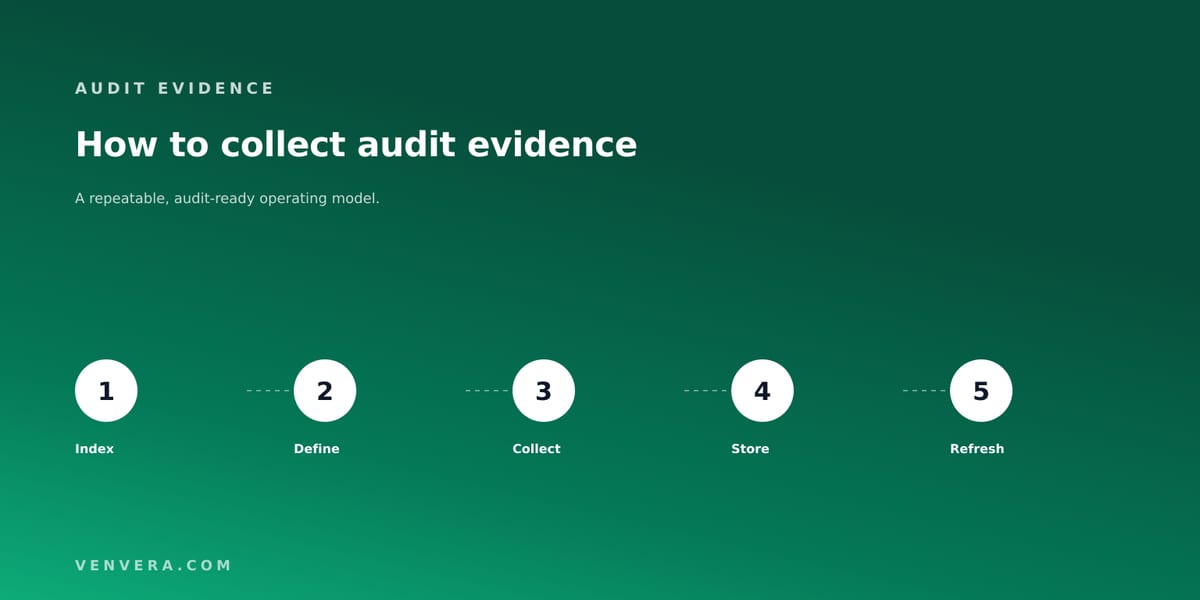
How to Collect Audit Evidence
Audit evidence is records, statements of fact and other verifiable information. How to collect it once, map it to controls and keep it current.

Learn
DORA Audit: What to Expect
There is no DORA certificate. A DORA audit is your supervisor using Article 50 powers, plus the internal audit Article 6(6) makes you run. What each asks for.

Learn
Cyber Resilience Act vs NIS2 vs DORA
The CRA regulates products, NIS2 regulates entities, and DORA replaces NIS2 for financial firms. Scope, dates, reporting clocks and fines side by side.

Learn
MiCA Fines and Penalties: What You Actually Risk
MiCA fines for companies start at EUR 5 million or 3% to 12.5% of turnover, and reach 15% for market abuse. Every Article 111 tier, and who imposes each.

Learn
How Long Does NIS2 Compliance Take?
NIS2 compliance takes six to twelve months for most entities, up to 18 from a standing start. The phases, what sets the range, and what had to be ready first.

Learn
Cyber Resilience Act Scope: Who It Applies To
CRA scope turns on one Article 2 test: a product with digital elements whose use includes a data connection. The test, the definitions and the carve-outs.

Learn
CRA Penalties and Deadlines: What Applies When
Cyber Resilience Act penalties reach 15 million euros or 2.5% of turnover, but not all at once. Which fine can apply on which date, from 2026 to 2027.

Learn
Solvency II Pillar 2 Requirements Explained
Solvency II Pillar 2 is the system of governance in Articles 41 to 49: risk management, ORSA, key functions, fit and proper, outsourcing. What each asks for.

Learn
MiCA Compliance Cost After 1 July 2026
MiCA prices exactly one thing: capital. Annex IV sets EUR 50 000 to EUR 150 000, and the fixed overheads test quietly overtakes it sooner than most expect.

Learn
EU AI Act: Provider vs Deployer
Article 3 defines the two roles, Article 16 and Article 26 set what each owes, and Article 25 turns one into the other. What each side has to hold.

Learn
EU AI Act Article 6: High-Risk Classification
Article 6 has two routes into high risk and one derogation with four conditions. What the 2026 Omnibus changed in it, and the dates that now apply.

Learn
UAE IA Requirements: What Entities Must Do
The UAE IA Regulation sets 15 control families, four priority levels and a set of always applicable controls. What each one asks of a designated entity.

Learn
Nigeria NDPA Fines and Penalties Explained
NDPA penalties reach the greater of 10 million naira and 2% of annual gross revenue. The 2% applies in both tiers, and only the naira floor changes.

Learn
EU AI Act Deadlines: Every Date That Applies
Every EU AI Act date after the 2026 amendment: what 2 August 2026 binds, where the high risk deadlines went, and the Article 111 transitionals.

Learn
EU AI Act Article 5: Prohibited Practices
Article 5 now lists ten lettered points, not eight. Regulation (EU) 2026/1744 inserted two more, and they start to apply on 2 December 2026.

Learn
What UAE IA Compliance Actually Costs
The UAE IA Regulation publishes no price. It publishes the mandates that create one: an always applicable core, justified exclusions, and P1 first.

Learn
Saudi NCA ECC Requirements Explained
ECC-2:2024 is 4 domains, 28 subdomains and 108 controls, not the 114 across 5 that most guides still quote. What each domain asks, and what 2024 moved.
Learn
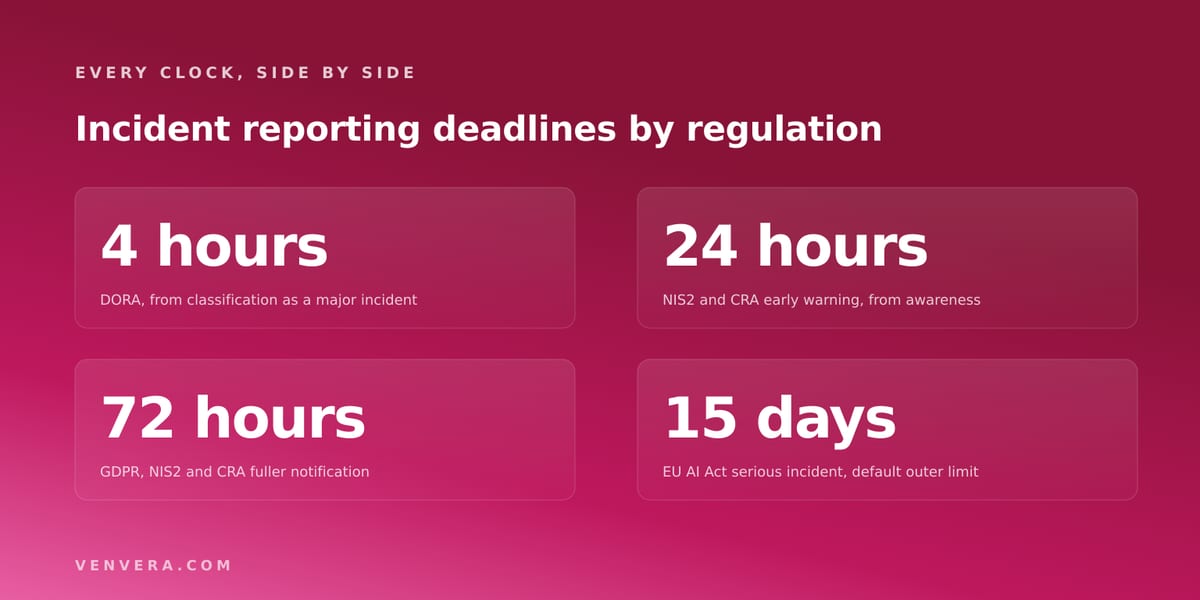
Incident Reporting Deadlines by Regulation
DORA gives you 4 hours, NIS2 24, GDPR 72 and the EU AI Act up to 15 days. Every clock, what starts it, and which one binds when several apply at once.

Learn
Choosing a CRA Compliance Tool
What a CRA compliance tool must actually do: the five jobs, the 24 and 72 hour clock that rules out a spreadsheet, and 12 questions to put to any vendor.
Compare
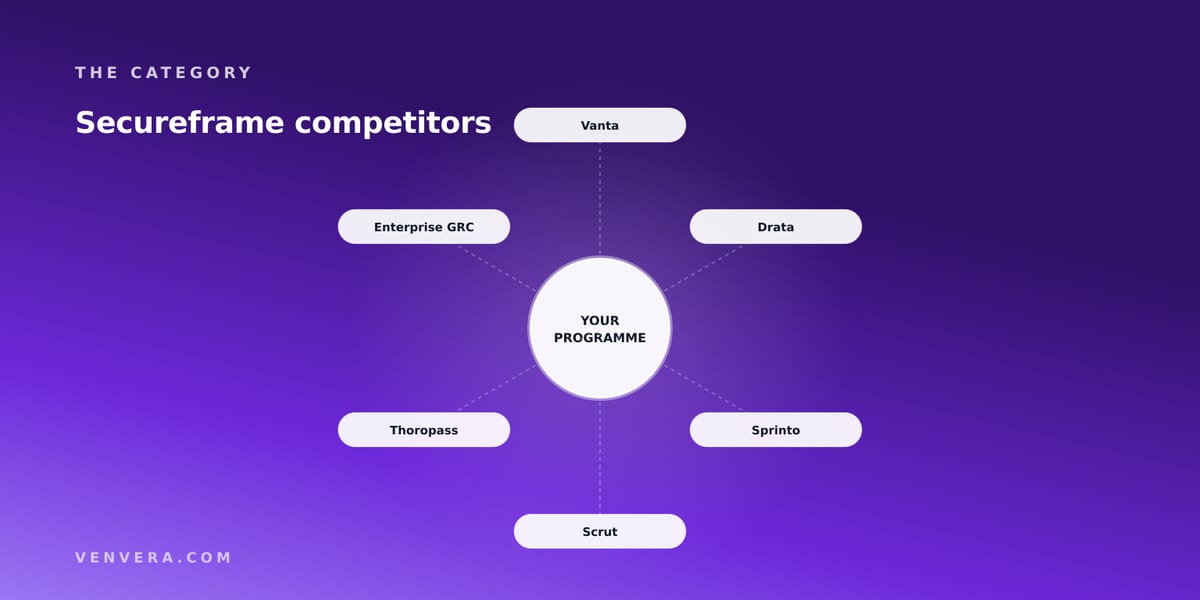
Secureframe Competitors: Who Competes on What
Every page ranking for this query was written by someone selling an alternative. Here is the category mapped by job, and what you can verify yourself.

Learn
SAMA CSF Requirements Explained
The SAMA Cyber Security Framework sets four domains, 32 subdomains and maturity level 3 as the floor. What each domain asks for, and what SAMA raised.

Learn
SAMA CSF Compliance Cost: What Drives It
SAMA never published a price for CSF compliance. It published the mandates that create one: a cleared full time CISO, maturity level 3, annual pen tests.

Learn
NIS2 Audit: What to Expect
Essential entities can be audited with no incident first, important entities only after evidence of a breach. What Articles 32 and 33 actually allow.

Learn
Cyber Resilience Act Compliance Cost
The Commission put CRA compliance at EUR 29 billion across 615,272 manufacturers. Do the division: about EUR 47,000 each, and here is where it goes.

Learn
eIDAS 2.0 Compliance Cost: What to Budget
The Commission priced a relying party's first year at EUR 60,000 to 70,000. What that estimate covers, what it leaves out, and how to size your own.

Learn
Cyber Resilience Act Fines and Penalties
CRA fines reach 15 million euros or 2.5% of worldwide annual turnover, whichever is higher. The three tiers, what triggers each, and who issues them.

Learn
Cyber Resilience Act Compliance Timeline
How long does Cyber Resilience Act compliance take? For most manufacturers 12 to 24 months. The phases, what drives the range, and the date to plan against.
Compare
Drata Competitors: The Category, Honestly Mapped
Drata's competitors split into four groups that compete on different things. Work out which group your problem belongs to before you compare a single feature.

Learn
EU AI Act Compliance Cost: What It Depends On
The Act prices roles and risk classes, not companies. What the cost is made of, where the quoted figures came from, and the step that removes most of it.

Learn
Vendor Security Questionnaires: A Guide
Questionnaires come back late for three fixable reasons. How to size one to the supplier, send it so it gets answered, and stop chasing by hand.

Learn
Third-Party Risk Management Process Flow
The flow is simple and it stalls in the same place every time: waiting on the supplier. Where each stage hands off, and how to stop the queue building.

Learn
How to Perform a Third-Party Risk Assessment
Assessing every supplier the same way is why most programmes stall. Tier first, set depth by tier, and the work becomes finishable. Seven steps.
Learn
How to Create a Risk Register
A risk register that survives an audit needs two scores, a named owner and a link to controls. The seven steps, the columns, and the mistakes to avoid.
Learn
Automated Access Review Software Explained
What actually gets automated in an access review, what has to stay human, and how to tell the difference before you buy. With the scoring model in full.

Learn
EU AI Act AI Literacy Requirements
Article 4 already applies, it binds providers and deployers alike, and it is the cheapest EU AI Act obligation to satisfy and to evidence.

Learn
NIS2 vs ISO 27001: How They Overlap
ISO 27001 covers much of what NIS2 asks for, and satisfies none of it by itself. Where the overlap is real, and the four gaps certification leaves.

Learn
EU AI Act Penalties and Fines Explained
Article 99 sets three tiers, up to 35M EUR or 7% of worldwide turnover. The rule for SMEs inverts the usual formula, and most summaries get it wrong.
Compare
Vanta vs Delve: What a Buyer Can Verify
Delve sells speed and Vanta sells breadth. After the events of 2026, the more useful comparison is which claims a buyer can independently check.
Compare
Delve Alternatives: A Buyer's Guide
If you are re-evaluating Delve, here is what has been reported, what is still only alleged, and how to pick a replacement you can actually verify.

Learn
EU AI Act Policies and Documentation
The EU AI Act asks for a document set rather than a policy. Here is what a high-risk provider has to be able to produce, article by article.
Compare
Sprinto vs Vanta: Which One Fits
Sprinto is the lighter option and Vanta the more complete one. The right answer depends on team size, integration needs and how many frameworks you run.
Compare
Secureframe vs Drata: Which Fits You
Secureframe and Drata overlap almost completely on the audit standards. The deciding factors are defense-sector work, integrations and your renewal price.
Compare
Vanta Alternatives: Compared on Fit
Most Vanta alternatives are the same product with a different logo. The ones worth your time differ on price transparency, regimes covered or weight.
Compare
Drata vs Vanta: An Honest Comparison
Drata and Vanta are close enough that most buyers decide on commercial terms. Here is where they genuinely differ, and when neither is the right answer.
Compare
A Drata Alternative for EU Compliance
US-first compliance platforms answer to auditors. EU regimes ask you to file with a regulator. Where that difference changes which tool fits you.
Compare
Drata Alternatives: An Honest Comparison
Drata is strong at what it was built for. The useful question is which alternative fits your regimes, your data residency and your pricing tolerance.

Learn
NIS2 Compliance Cost: What to Budget
Germany priced NIS2 for its own economy: about 2.1bn one-off and 2.2bn a year across 30,000 entities. Here is what that arithmetic means for your budget.

Learn
How Long Does DORA Compliance Take?
DORA has applied since January 2025, so the real question is how long from a standing start. The honest answer, phase by phase, with the long pole named.

Learn
NIS2 Fines and Penalties: What You Actually Risk
NIS2 sets minimum ceilings: EUR 10M or 2% of turnover for essential entities, 7M or 1.4% for important ones, plus personal liability for managers.

Learn
DORA Compliance Cost: A Line-by-Line Model (2026)
Published DORA cost estimates disagree by orders of magnitude. Here is the line-by-line model that produces your number, work item by work item.
Best
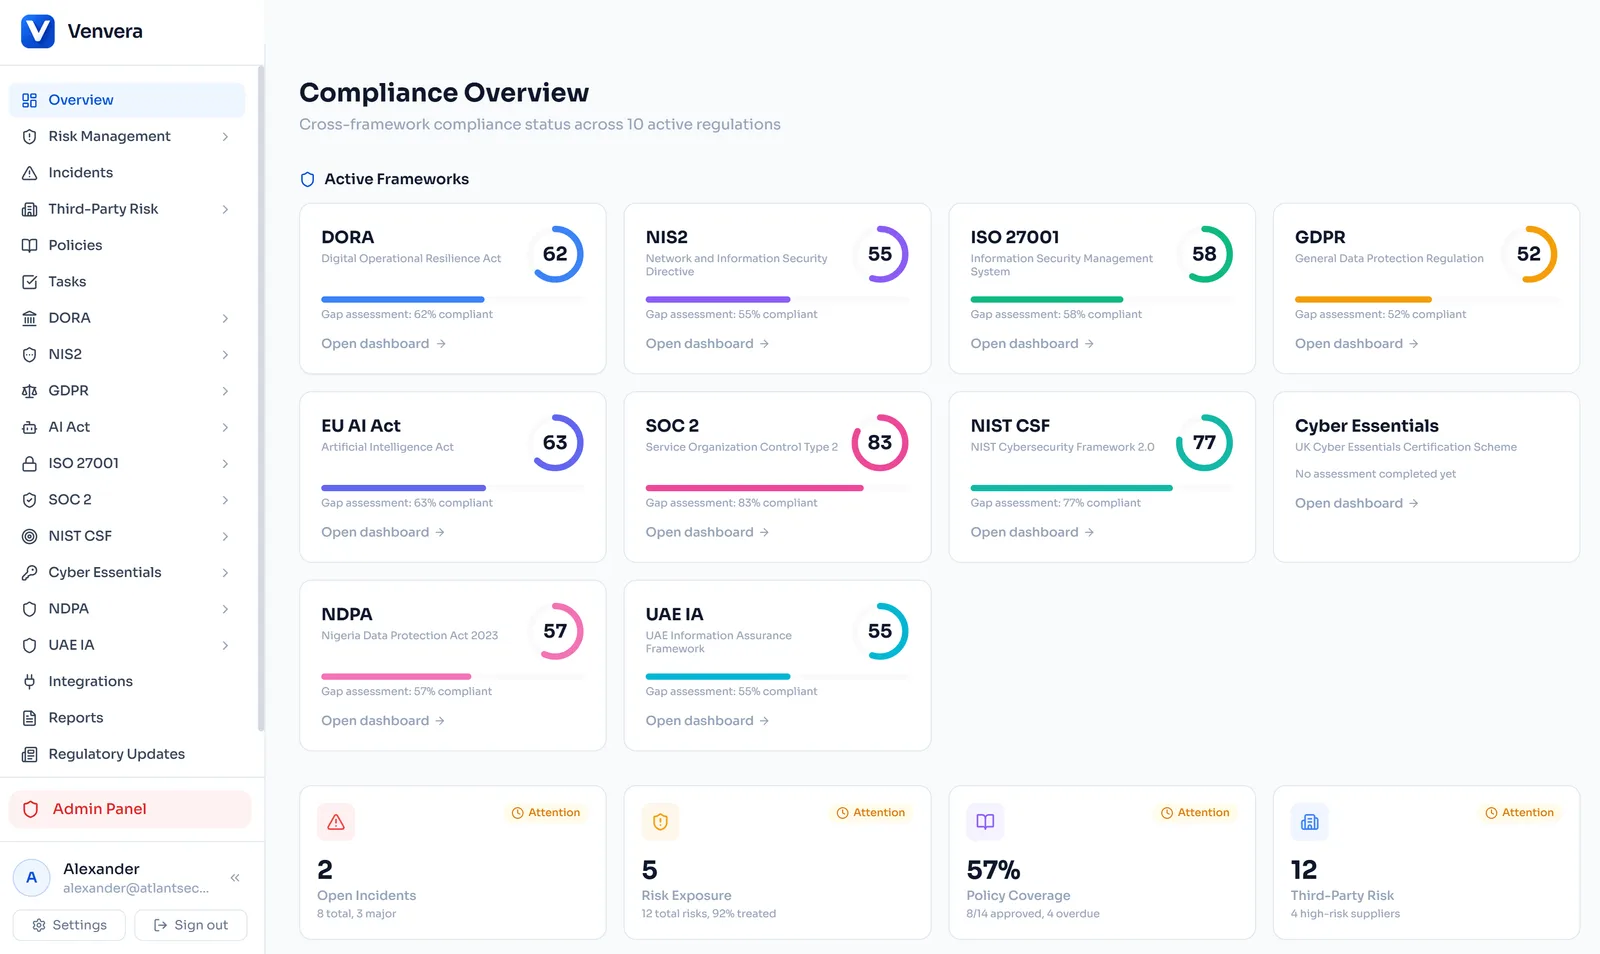
GRC Software for GCC Companies (2026)
Choosing GRC software in the GCC: start from framework overlap, check the regional control sets are actually maintained, and ask about residency precisely.
Learn
Bilingual Policies and Evidence for Gulf Regulators
How to run Arabic and English compliance documentation together: which language binds, what needs translating, fixed terminology and per-document language.
Best
SAMA CSF Compliance Software (2026): Buyer Guide
SAMA CSF compliance software for 2026: the real control structure, maturity scoring, evidence freshness, and the overlap with ISO 27001 and PCI DSS.
Best
Risk Management Software in Arabic (2026)
Risk management software in Arabic: bilingual registers, Arabic sorting and scoring, what SAMA and the NCA expect, and how risks stay linked to controls.
Best
Arabic Compliance Software (2026): What to Check
Arabic compliance software compared for 2026: right to left layout, bilingual policies and evidence, Arabic exports, and the Gulf frameworks that matter.

Learn
NIS2 Solutions for Banks: What Applies vs DORA
NIS2 solutions for banks: why DORA is the operative regime, where NIS2 still applies across the group, and what your platform must do. Reviewed July 2026.
Resources
eIDAS 2.0 Readiness Checklist (Free Excel, 2026)
The free eIDAS 2.0 Readiness Checklist maps 24 QTSP and relying-party steps for the EU Digital Identity Wallet and updated trust services. Reviewed July 2026.

Resources
Solvency II ORSA Checklist (Free Excel, 2026)
Free Solvency II ORSA checklist in Excel: assess your System of Governance and ORSA process against Pillar 2 requirements. 45 items. Reviewed July 2026.

Resources
Nigeria NDPA Compliance Checklist (Free, 2026)
A free NDPA compliance checklist for Nigeria's Data Protection Act 2023 and 2025 GAID: 60 items on DPO, lawful basis, breaches and DPIAs. Reviewed July 2026.
Resources
UAE IA Checklist: 134 Controls (Free Excel, 2026)
Free UAE IA checklist: all 134 controls of Information Assurance Standard v2 with priority, applicability, status, evidence and owner. Updated August 2026.
Resources
CMMC Self Assessment Checklist (Free Excel 2026)
A free 63-item CMMC self assessment checklist in Excel: score each Level 2 practice, map gaps to your POA&M, and prep for a C3PAO review. Reviewed July 2026.
Resources
NIST CSF 2.0 Assessment Template (Free Excel, 2026)
Free NIST CSF 2.0 assessment template: an Excel workbook scoring current vs target across all six Functions and the 92 Subcategories. Reviewed July 2026.
Resources
Cyber Essentials Checklist (Free Excel, 2026)
Free Cyber Essentials checklist: self-assess the five technical controls before you certify or bid for UK public-sector contracts. Reviewed July 2026.

Resources
Cyber Resilience Act Compliance Checklist (Free Excel)
Free Cyber Resilience Act compliance checklist: 24 Excel items covering Annex I requirements, SBOM and vulnerability reporting to ENISA. Reviewed July 2026.
Resources
EU AI Act Compliance Checklist (Free Excel, 2026)
Free EU AI Act compliance checklist in Excel: classify your AI system by risk tier and check the 62 high-risk provider obligations. Reviewed July 2026.
Resources
Vendor Risk Assessment Template (Free Excel, 2026)
Download a free vendor risk assessment template covering data, subprocessors, certifications, access, encryption, incidents and exit. Reviewed July 2026.
Resources
Incident Response Plan Template (Free Excel, 2026)
A free Excel incident response plan template with GDPR, NIS2, DORA and EU AI Act notification deadlines, plus a ready incident log. Reviewed July 2026.
Resources
Risk Register Template (Free Excel, 2026)
Free information security risk register template in Excel: likelihood x impact scoring (1-25), treatment options, owners, residual risk. Reviewed July 2026.
Resources
GDPR RoPA Template (Free Excel, 2026)
Free GDPR RoPA template with the Article 30(1) columns and a filled example row. Build your Record of Processing Activities correctly. Reviewed July 2026.
Resources
DPIA Template (Free Excel, 2026)
Free DPIA template following GDPR Article 35(7): describe processing, test necessity and proportionality, and score risks and measures. Reviewed July 2026.
Resources
GDPR Compliance Checklist (Free Excel, 2026)
Free Excel GDPR compliance checklist: 51 items covering lawful basis, data subject rights, RoPA, security, breach, DPIA and transfers. Reviewed July 2026.
Resources
NIS2 Compliance Checklist (Free Excel, 2026)
Free Excel NIS2 compliance checklist: 48 items across scope, the Article 21 measures, and Article 23 reporting deadlines. Find your gaps. Reviewed July 2026.
Resources
PCI DSS Compliance Checklist (Free Excel, 2026)
Free PCI DSS compliance checklist: all 12 requirements of PCI DSS v4.0.1 in 70 items with status columns, including March 2025 controls. Reviewed July 2026.

Resources
HIPAA Risk Assessment Template (Free Excel, 2026)
Free Excel HIPAA risk assessment template with 65 items mapped to 45 CFR 164.308-312 for the mandatory HIPAA Security Rule risk analysis. Reviewed July 2026.
Resources
SOC 2 Readiness Checklist (Free Excel, 2026)
A free SOC 2 readiness checklist: a 72-item Excel workbook scoring all five Trust Services Criteria with status, evidence, owner columns. Reviewed July 2026.

Resources
ISO 27001 Statement of Applicability Template (Excel, 2022)
Free ISO 27001 Statement of Applicability template: all 93 Annex A controls from the 2022 revision, ready to fill in. Editable Excel. Reviewed July 2026.
Best
Venvera as an Alternative to Vanta for a Trust Center
An honest look at Venvera versus Vanta for building a trust center: where Vanta wins, where an EU-hosted flat-priced option fits better. Reviewed July 2026.
Best
Venvera as an Alternative to Vanta for PCI DSS
An honest look at Venvera versus Vanta for PCI DSS: where each wins, why EU hosting and ISO 27001 overlap matter, and the ASV caveat. Reviewed July 2026.
Best
Venvera as an Alternative to Vanta for SOC 2
An honest look at Venvera versus Vanta for SOC 2: where Vanta still wins, and where EU data residency and flat pricing favor Venvera. Reviewed July 2026.

Best
Venvera as an Alternative to Vanta for ISO 27001
An honest comparison of Venvera and Vanta for ISO 27001: where each wins on automation, EU hosting, crosswalked evidence and pricing. Reviewed July 2026.

Best
Venvera as an Alternative to Vanta for HIPAA Compliance
An honest, fact-checked comparison of Venvera and Vanta for HIPAA: where each wins, EU data residency, HIPAA plus GDPR, and flat pricing. Reviewed July 2026.
Best
7 Best PCI DSS Compliance Software (2026)
PCI DSS compliance software compared for 2026: coverage, crosswalks, EU data residency and honest pricing across 7 platforms. Reviewed July 2026.

Best
7 Best HIPAA Compliance Software (2026)
HIPAA compliance software compared: 7 platforms for evidence, risk analysis and Security Rule readiness, with honest pros and cons. Reviewed July 2026.

Learn
ISO 27001 Annex A: How the 93 Controls Are Organised
How ISO 27001:2022 Annex A is organised: the four themes, what changed from 2013, how the Statement of Applicability selects controls, and who has to comply.

Learn
What Is SOC 2? Type 1 vs Type 2, Explained
SOC 2 explained: what the AICPA attestation report is, the five Trust Services Criteria, Type 1 vs Type 2, and which SaaS vendors need it. Reviewed July 2026.

Learn
PCI DSS: Who Must Comply and Which SAQ Applies
PCI DSS applies to any business that stores, processes or transmits cardholder data. Learn who must comply and which SAQ fits your setup. Reviewed July 2026.

Learn
What Is HIPAA Compliance? Covered Entities and BAAs
HIPAA compliance explained: covered entities, business associates, BAAs, the Privacy, Security and Breach Notification Rules, penalties. Reviewed July 2026.

Learn
What Is NIS2 and Who Must Comply in 2026?
What is NIS2 and who must comply? The 2026 scope guide: sectors, size thresholds, essential vs important, obligations and penalties. Reviewed July 2026.
Best
Vanta Alternative for EU AI Act Compliance (2026)
A Vanta alternative for the EU AI Act: Vanta is strong on governance; high-risk conformity needs FRIA, the technical file and GPAI. Reviewed July 2026.
Best
Vanta Alternative for GDPR Compliance (2026)
A Vanta alternative for GDPR, compared honestly: Vanta is capable, so it comes down to EU data residency, the breach clock and pricing. Reviewed July 2026.

Best
Vanta Alternative for Third-Party Risk Management (2026)
A Vanta alternative for third-party risk: assess a vendor once, satisfy NIS2, ISO 27001, DORA and GDPR from one register. Reviewed July 2026.
Best
Vanta Alternative for NIS2: The Operator's Comparison (2026)
A Vanta alternative for NIS2, compared honestly: what the Directive demands, where Vanta's ISO mapping gaps, and how to get ready. Reviewed July 2026.

Best
6 Best Cyber Resilience Act Compliance Software (2026)
The best Cyber Resilience Act compliance software for 2026, ranked before the 11 Sep reporting deadline. Honest cons, published pricing. Reviewed July 2026.

Learn
eIDAS Compliance Software: An eIDAS 2.0 Buyer's Guide
eIDAS compliance software compared: the three product categories buyers confuse, and what a real eIDAS 2.0 governance layer must cover before 2027.

Learn
The Cyber Resilience Act Deadlines: 2026 and 2027
CRA reporting obligations start on 11 September 2026 and the regulation applies in full on 11 December 2027. The complete timeline and what binds when.

Learn
Who Must Comply With the Cyber Resilience Act?
CRA scope follows the product, not the sector. The digital-elements test, the three economic operators, Annex III and IV, and the 2026 and 2027 deadlines.
Learn
How to Become Compliant: A Step-by-Step Guide (2026)
How to become compliant without drowning in spreadsheets: find which rules apply, run a gap analysis, remediate, collect evidence once, pass the audit.

Learn
The eIDAS 2.0 Deadline: What Happens by 24 December 2027
By 24 December 2027, private relying parties that require strong authentication must accept the EU Digital Identity Wallet. Who it binds, and the timeline.

Learn
eIDAS 2.0 Scope: Who Must Accept the EUDI Wallet?
Use this role-based decision tree to see when eIDAS 2.0 applies, when EUDI Wallet acceptance is mandatory, and which SME exemptions matter.
Best
DORA Compliance Solutions for Banks: The Honest Comparison
DORA solutions for banks compared the way a buyer would: consultants, legacy GRC, audit SaaS, spreadsheets and Venvera. Who should buy what, with the maths.

Features
Compliance Software for Groups of Companies
Compliance software for a group of companies or holding structure: author policies once at the parent, each subsidiary proves them with its own evidence.
Learn
Solvency II Software: A Pillar 2 Buyer's Guide
Solvency II software compared: the three tool categories, what a Pillar 2 governance platform needs, and how a crosswalk cuts duplicate work.
Best
Vanta vs Venvera for Risk Management: An Honest Comparison
Vanta vs Venvera for risk management: risk register, inherent and residual scoring, heatmaps, risk appetite and KRIs, compared claim by claim.

Learn
EU AI Act vs DORA: Comply With Both, One Programme
EU AI Act and DORA overlap in five zones. Run both from one compliance programme instead of two, and see exactly where the requirements meet.
Learn
EU AI Act High-Risk Deadline: Why 2 August 2026 Moved to 2027
The August 2026 high-risk deadline moved to December 2027 for standalone systems. What still binds in 2026, and what high-risk providers must build now.
Learn
EU AI Act Conformity Assessment for High-Risk AI in Financial Services
Article 43 conformity assessment for high-risk financial AI, covering credit scoring and insurance pricing, and why the deadline moved to December 2027.

Learn
DORA vs NIS2: Key Differences and Who's Covered
DORA vs NIS2: two EU cyber regulations with confusingly close names and very different obligations. See which one applies to your organisation, and why.

Learn
DORA TLPT: Threat-Led Penetration Testing in 2026
DORA threat-led penetration testing under Articles 26 and 27: who gets designated, the TIBER-EU phases in RTS 2025/1190, and how to plan the engagement.
Features
Restricting Admin Access to Your Tenant Data
By default no Venvera engineer can open your tenant. Access happens only when your admin approves a time-boxed request. See the lockbox flow.
Best
Best KRI Software (2026): Key Risk Indicator Tools
The best KRI software for 2026, compared: key risk indicator tracking, RAG thresholds, board reporting, honest cons and flat pricing. Reviewed July 2026.

Learn
DORA Key Risk Indicators: Article-by-Article Guide
Fourteen DORA key risk indicators, each mapped to the article of Regulation 2022/2554 it helps evidence, with every article number checked against the text.
Learn
Key Risk Indicators (KRIs): 14 to Track in 2026
Key Risk Indicators explained for CISOs and CROs, with thresholds, formulas and a 14-KRI starter pack mapped to ISO 27001, NIS2, DORA and NIST CSF.
Best
Vanta vs Venvera for DORA: RoI, Reporting and Fit
Vanta vs Venvera for DORA, compared honestly: Register of Information, xBRL-CSV export, ICT incident reporting and EU hosting. Every claim evidenced.

Best
Best NCA ECC Compliance Software (2026): ECC-2:2024
The best NCA ECC compliance software for 2026 (ECC-2:2024): control mapping, an ISO 27001 crosswalk, honest cons and flat pricing. Reviewed July 2026.
Best
6 Best NIS2 Compliance Software for Startups (2026)
The 6 best NIS2 compliance software options for startups in 2026, ranked on price and speed to audit-ready: Venvera, Vanta, Drata, Sprinto and more.
Best
6 Best GDPR Compliance Software for SaaS (2026)
The 6 best GDPR compliance software for SaaS in 2026, compared on RoPA, DPIAs and breach workflows. EU-hosted options included.

Learn
ISO 42001 vs EU AI Act: Do You Need Both?
One is voluntary certification, one is binding law. See exactly where they overlap so you build AI governance once, not twice, and what each requires.
Best
SOC 2 Software for SaaS Startups (2026)
The 5 best SOC 2 compliance software for SaaS companies in 2026, compared on price, automation and audit readiness: Vanta, Drata, Sprinto and more.

Learn
VARA Data Protection: UAE PDPL Rules for VASPs
VARA binds every VASP to the UAE PDPL, a mandatory DPO, and a notify-VARA step within 24 hours. What the Technology and Information Rulebook requires.
Learn
VARA Incident Reporting: The 72-Hour Clock
VARA's 72-hour notification runs from detection under Rule I.K.1. What triggers it, what the report must contain, and the 24-hour personal data clock.
Learn
VARA Key and Wallet Management: What the Rules Say
VARA key and wallet duties come in three tiers: four binding Rules in Part I Section D, Schedule 1 Guidance, and custody-only rules. What each one requires.
Learn
VARA Compliance Guide for Dubai VASPs 2026
What a Dubai VASP licence requires: the four compulsory rulebooks, 19 cybersecurity criteria, the 72 and 24 hour clocks, and the capital floors.
Learn
VARA Penetration Testing and Smart Contract Audits
Rule I.E.1 has two triggers, not one: at least annually AND before any new system, application or product ships. What VARA binds, and what is only Guidance.
Learn
VARA Cybersecurity Policy: The 19 Mandatory Criteria
VARA's rulebook lists 19 minimum cybersecurity policy criteria, not 18. Each in the rulebook's words, plus the two ISO 27001 templates always miss.
Learn
VARA CISO Appointment and Staff Competency Rules
VARA's CISO rule sits in the Technology and Information Rulebook. What Part I Sections I and J actually require of your compliance team, and what they do not.
Best
Best VARA Compliance Software (2026): For Dubai VASPs
The best VARA compliance software for 2026, compared for Dubai VASPs: Travel Rule handling, the Technology and Information Rulebook, and honest cons.

Learn
DORA Supervisory Assessments: 2026 Guide
DORA supervision is live. How it is structured across the NCAs and ESAs, what a supervisor can demand, and the evidence to have ready before they ask.
Learn
DORA Compliance Gap Assessment: EU Banks
Enforcement is live and supervisors keep flagging the same five DORA gaps at EU banks. See where they fail and how to close each before your assessment.
Learn
DORA 'Significant': The Critical ICT Provider Test
Will the ESAs designate your firm a critical ICT third-party provider? See the thresholds behind DORA's 'significant' test and where it bites.
Learn
DORA Operational Resilience Testing: Article 24
What DORA Article 24 really requires of a resilience testing programme, where the board approval duty comes from, and which quoted numbers are invented.
Learn
DORA Major Incident Classification: 7 Criteria
Do you owe your regulator a report in 4 hours? The exact test in Delegated Regulation 2024/1772, every threshold, and the 4h, 72h and 1-month clock.
Learn
DORA ICT Third-Party Risk: Build a Compliant Vendor Register
Build a DORA vendor register from scratch: the nine mandatory contract clauses, six more for critical functions, the subcontracting RTS and exit tests.

Learn
DORA ICT Risk Management Framework: Article-by-Article Guide
What DORA Chapter II and RTS 2024/1774 require an ICT risk management framework to contain, chapter by chapter, with every citation checked.
Best
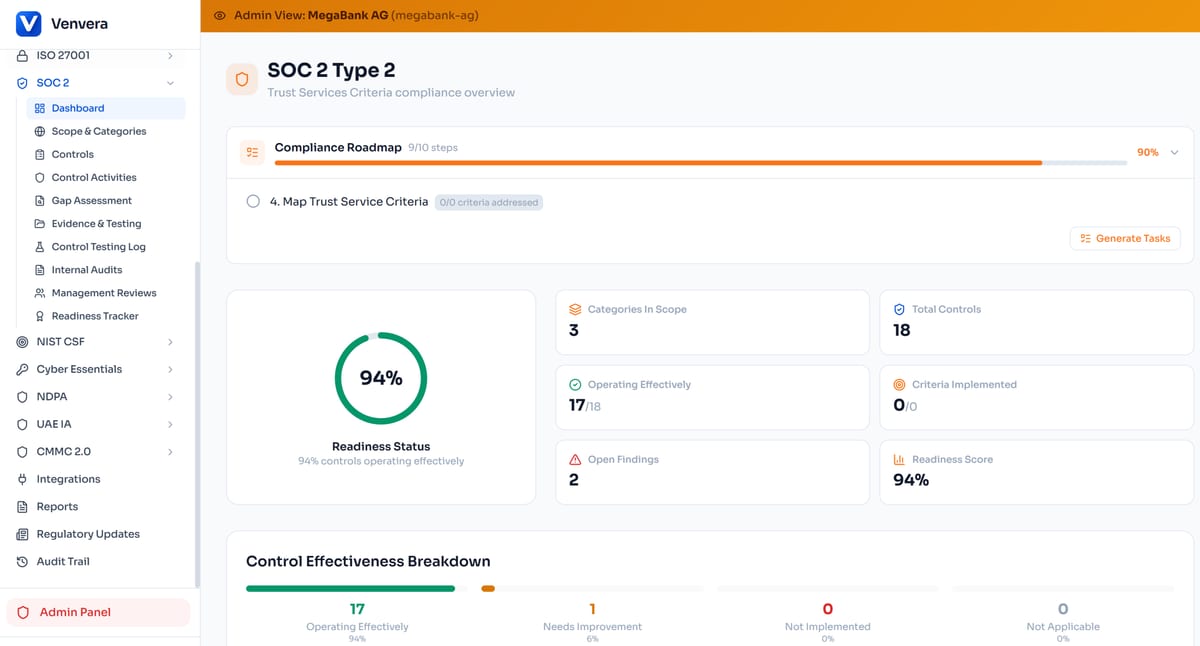
5 Best SOC 2 Compliance Software (2026)
The best SOC 2 compliance software in 2026, compared: honest cons, published pricing and an ISO 27001 control crosswalk. Reviewed July 2026.
Best
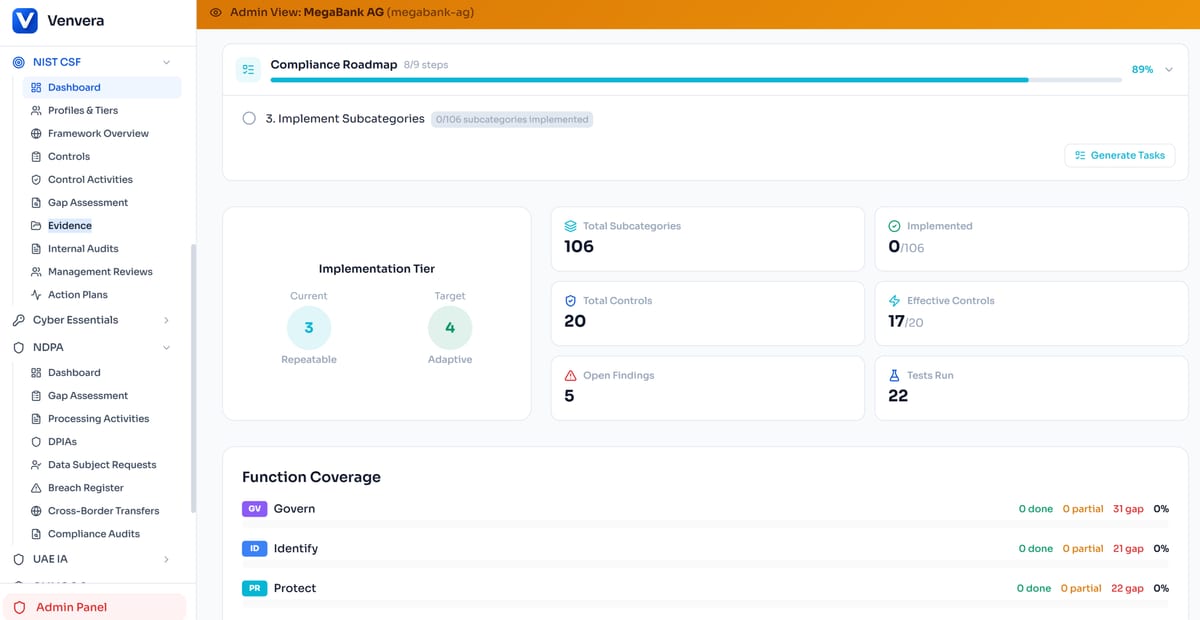
Best NIST CSF 2.0 Compliance Software (2026)
The best NIST CSF 2.0 compliance software for 2026: all six functions, a free controls spreadsheet, honest cons and flat pricing. Reviewed July 2026.
Best
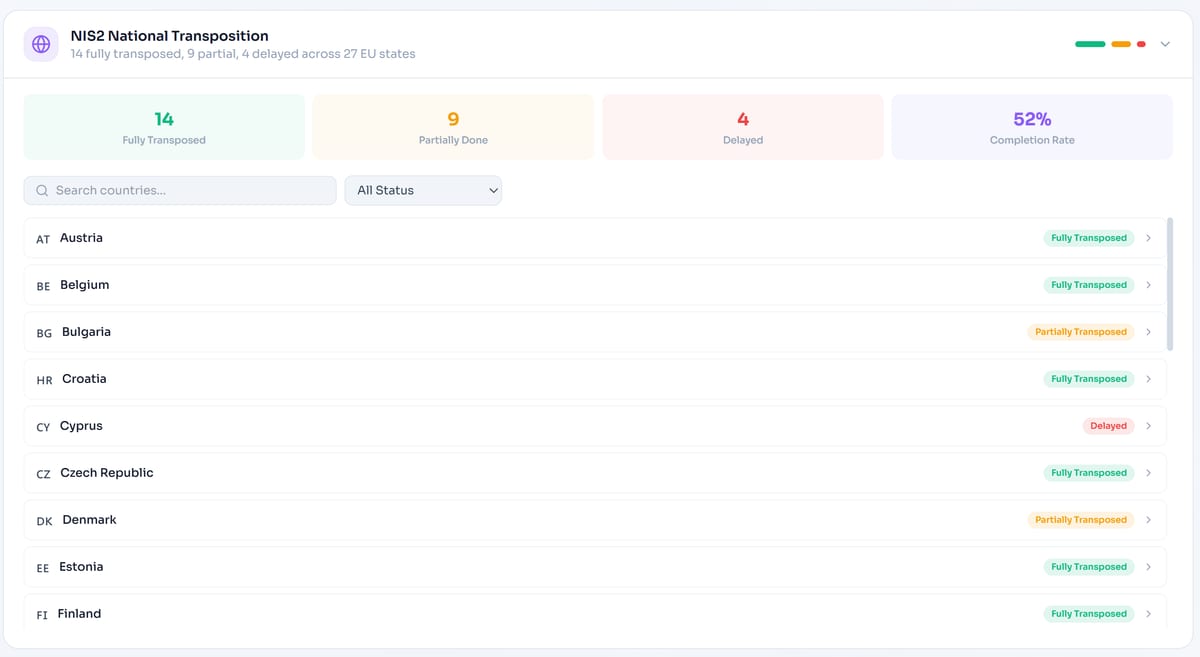
5 Best NIS2 Compliance Software (2026)
The best NIS2 compliance software for 2026: methodology, honest cons, EU data residency and Article 23 incident reporting built into the platform.

Best
Best NDPA Compliance Software (2026): Nigeria
The best NDPA compliance software for 2026, compared for Nigeria data protection: NDPC registration, CAR filing support and honest cons. Reviewed July 2026.

Best
5 Best ISO 27001 Compliance Software (2026)
Compare the best ISO 27001 compliance software for 2026: Annex A control depth, flat EU pricing and a SOC 2 crosswalk to do the work once. Reviewed July 2026.
Best
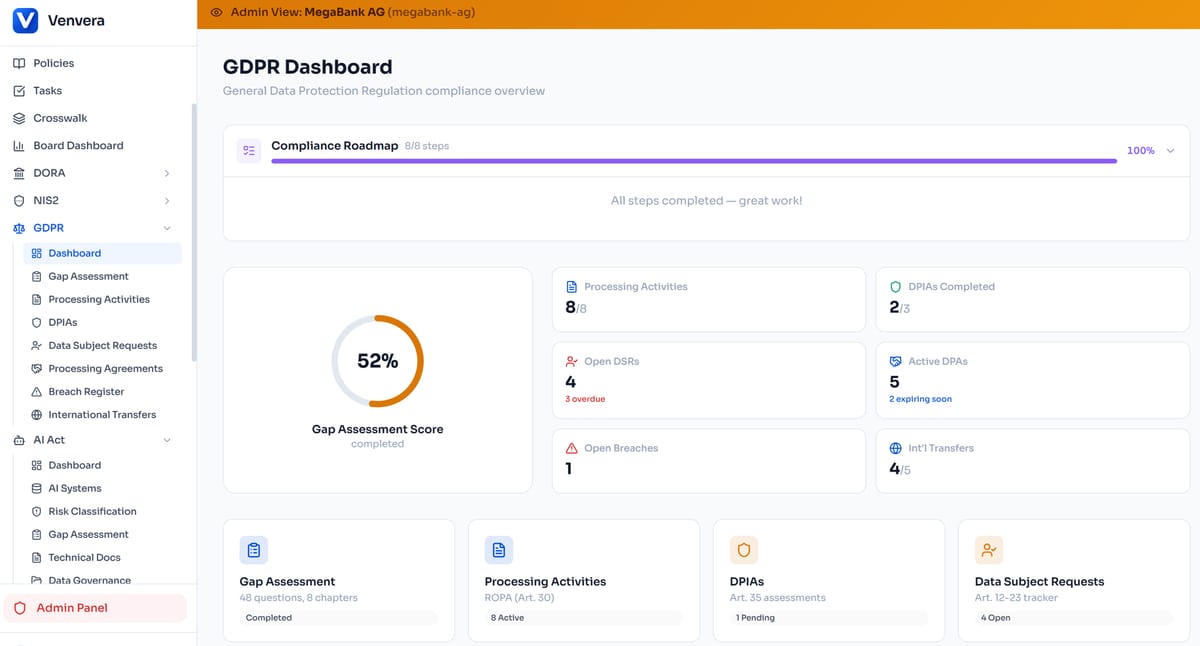
Best GDPR Compliance Software With EU Data Residency (2026)
The best GDPR compliance software with EU data residency for 2026: honest pros and cons, flat published pricing, DPIA and RoPA support. Reviewed July 2026.
Best
Best EU AI Act Compliance Software (2026)
Compare the best EU AI Act compliance software for 2026: risk classification, FRIA support, honest cons and flat EU pricing. Reviewed July 2026.
Best
Best Cyber Essentials Compliance Software (2026): UK Bids
The best Cyber Essentials compliance software for 2026, compared for UK bids: PPN 014, CE vs CE Plus, honest cons and flat pricing. Reviewed July 2026.
Best
Best CMMC 2.0 Compliance Software (2026): DoD Primes
The best CMMC 2.0 compliance software for 2026, compared for DoD primes and subs before the Phase 2 deadline: honest cons, flat pricing. Reviewed July 2026.
Best
5 Best DORA Compliance Software (2026)
The best DORA compliance software for 2026: honest pros and cons, published EU pricing, and the Register of Information xBRL-CSV angle buyers overlook.
Best
Best UAE IA Compliance Software (2026): 134 Controls
UAE IA compliance software compared for 2026: which platforms cover the 134 controls of Standard v2, which handle the 39 P1 controls, and how each one fits.

Compare
Vanta Alternative for EU Compliance: An Evidence-Based Comparison
A Vanta alternative for EU compliance: xBRL-CSV register submission, multi-regime incident classification, per-country NIS2 rules and published pricing.

Features
Board-Level Compliance: 6 New Platform Features
Board-level compliance gets 6 new features: personal liability tracking for NIS2 and DORA, AI policy drafting, and risk-based vendor management.

Features
Multi-Framework Compliance: 5 Features That Work
Multi-framework compliance works when one control counts everywhere: crosswalk propagation, evidence stored once, one incident classified across regimes.

Features
How Venvera Speeds Up GRC Processes
Kill GRC spreadsheet sprawl: map controls once, reuse them across every framework you run, keep evidence linked, and shorten audit preparation.
Features
What Is Venvera? Multi-Framework GRC Platform
Venvera kills the compliance spreadsheet: collect evidence once, stay audit-ready across ISO 27001, NIS2, DORA and more on EU data residency.
Learn
EU AI Act for Healthcare: Which AI Must Comply
Most medical and diagnostic AI is high-risk under the EU AI Act. Which systems fall under Annex I or Annex III, and what each route demands by 2027.

Learn
Does the EU AI Act Apply Outside the EU?
Selling AI into the EU from outside it usually puts you in scope. The output-used-in-the-EU trigger, the authorised representative rule and the deadlines.

Learn
EU AI Act: Who's in Scope and the 2025-28 Deadlines
Does the EU AI Act apply to you? Map your systems to the risk tiers and the 2025 to 2028 deadlines, including high-risk moving to 2 December 2027.
Learn
DORA Gap Assessment: Score Your Readiness
Score your DORA readiness across seven domains, each anchored to the article it comes from, then weight the gaps so you know what to fix first.
Learn
DORA Register of Information: 15 Official Templates Explained
The DORA Register of Information explained: all 15 templates from Implementing Regulation 2024/2956, how they connect, and how to file one clean submission.
Learn
Why Your DORA Register of Information Gets Rejected
The seven ESA rule codes that actually reject a Register of Information submission, what causes each one, and how to clear the validation cascade.

Best
Best Compliance Management Software (2026): Multi-Framework
The best compliance management software for 2026 compared: multi-framework coverage, a control crosswalk, flat published pricing and honest cons on each.

Learn
DORA Register of Information Software Ranked
Your Register of Information is regulatory data, not a spreadsheet. Compare the tools that export clean XBRL OIM-CSV your NCA accepts on the first try.