Skip to framework content
NEWVenvera speaks your language: the full platform, in English, German, Spanish, Bulgarian, Arabic and Chinese.See what’s new →

CMMC compliance software

Prepare for CMMC one practice at a time.

Organise CMMC practices, evidence and plans of action in one workspace. Give your team a clear view of readiness for the assessment your contract requires.

14-day Professional trial · no credit card required

Inside VenveraProduct preview
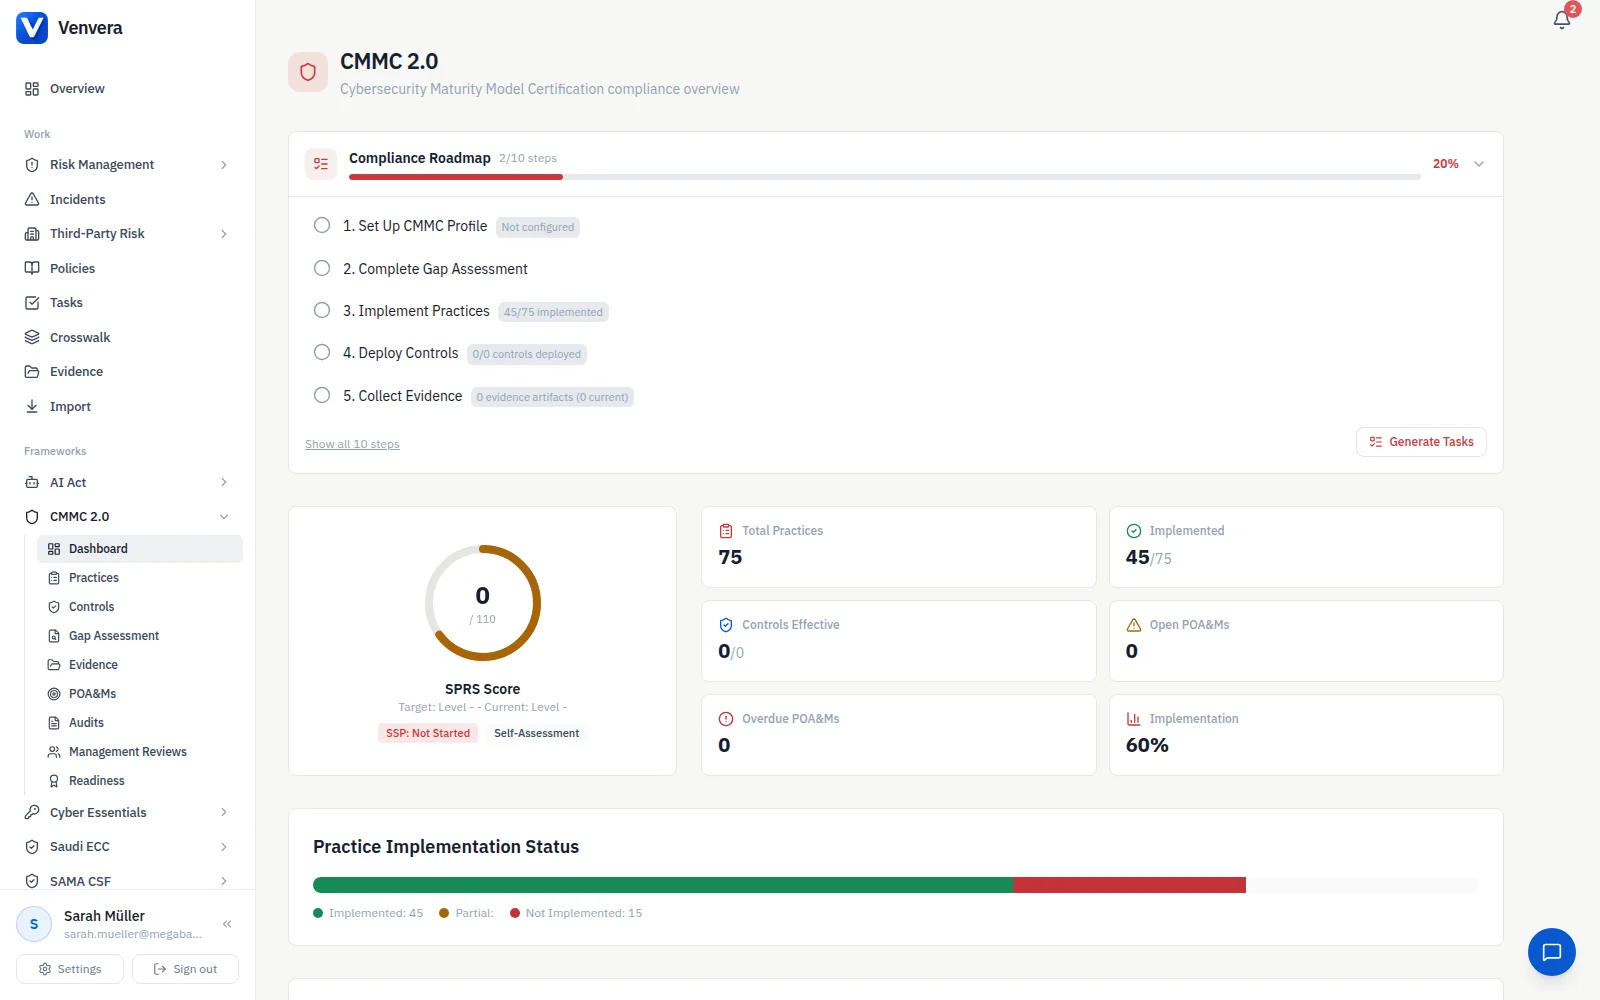
CMMC workspace: practice coverage and assessment preparation.
Real product screen · example dataExplore the workflow

A practical way to move forward

Know the work. See the progress.

One workspace for the requirements, the people doing the work and the records behind your next review.

Practices

Know what your team needs to demonstrate.

Review the practices for your programme and track implementation. Keep the work anchored to specific requirements instead of a general security checklist.

  • CMMC practice library
  • Control implementation records
Evidence & POA&Ms

Keep gaps and proof together.

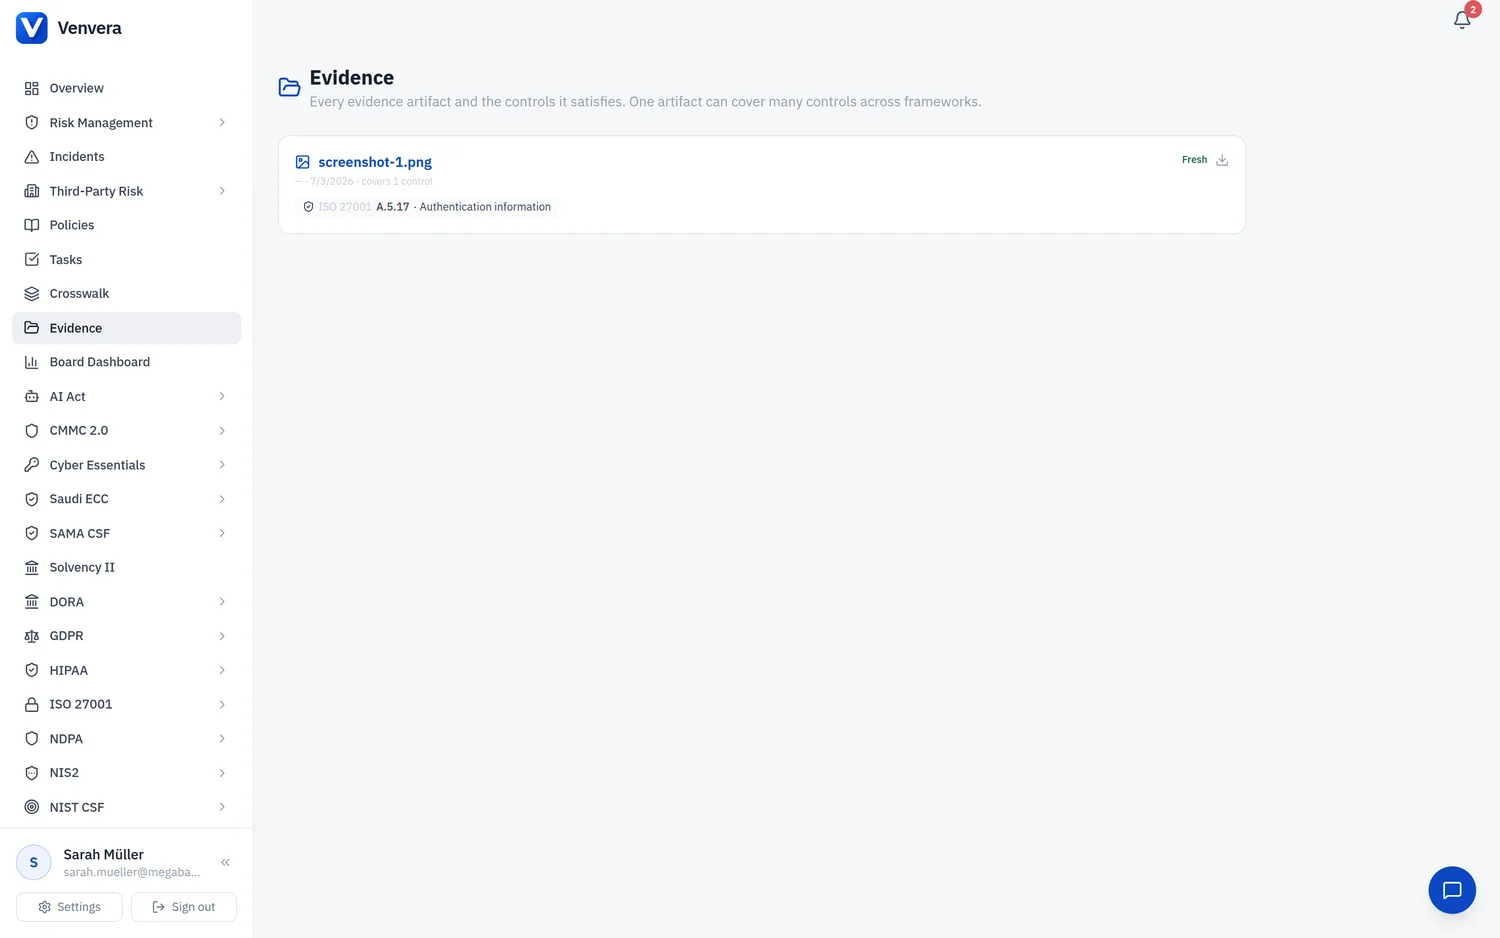
Organise evidence and track plans of action and milestones. Keep unresolved items visible while you confirm which items are eligible under your assessment rules.

  • Practice-linked evidence
  • Plans of action and milestones
Assessment preparation

Make the next review easier to run.

Use readiness, audit and review records to coordinate preparation. Give the team a working picture of progress before the formal assessment process.

  • Readiness and gap assessment
  • Audit and review tracking

The detail behind the dashboard

Give every review a better starting point.

Move from a progress summary to the records that support it. Keep the next conversation focused on the work that needs attention.

Screens show example data. Shared platform features and availability depend on your plan.

See it with our team
Shared evidence workspace: organise material for control and practice reviews.
Shared evidence workspace: organise material for control and practice reviews.Open full size

Start with the right scope

For defence contractors and suppliers preparing for CMMC.

CMMC requirements depend on the information handled and the requirement in the relevant solicitation or contract. Confirm the required level, assessment type and scope before planning your preparation.

Department of Defense: about CMMC (opens in a new tab)

Use the work you already have

Find the overlap. Review the gaps.

Explore shared requirements and download a CSV. A mapping identifies related work; it does not certify compliance.

Explore CMMC control mappings
You already run
You have been asked to add
15 of the 55 domains in this crosswalk appear in both ISO 27001 and CMMC 2.0.
DomainISO 27001CMMC 2.0
Encryption
A.8.24Use of cryptography
SC.L2-3.13.8CUI Encryption in Transit
SC.L2-3.13.11FIPS-Validated Cryptography for CUI
Access Control
A.5.15Access control
AC.L2-3.1.1Authorized Access Control
AC.L2-3.1.2Transaction & Function Control
AC.L2-3.1.3Control CUI Flow
Identity Management
A.5.16Identity management
IA.L2-3.5.1Identification
IA.L2-3.5.2Authentication
Authentication & MFA
A.5.17Authentication information
A.8.5Secure authentication
IA.L2-3.5.3Multi-Factor Authentication
Access Rights Review
A.5.18Access rights
AC.L2-3.1.5Least Privilege
Privileged Access Management
A.8.2Privileged access rights
AC.L2-3.1.5Least Privilege
Network Security
A.8.20Networks security
A.8.21Security of network services
A.8.22Segregation of networks
SC.L2-3.13.1Boundary Protection
Vulnerability Management
A.8.8Management of technical vulnerabilities
RA.L2-3.11.2Vulnerability Scan
Logging & Monitoring
A.8.15Logging
A.8.16Monitoring activities
AU.L2-3.3.1System Auditing
AU.L2-3.3.2User Accountability
Incident Management
A.5.24Information security incident management planning and preparation
A.5.25Assessment and decision on information security events
A.5.26Response to information security incidents
IR.L2-3.6.1Incident Handling
IR.L2-3.6.2Incident Reporting
Risk Assessment
A.5.7Threat intelligence
RA.L2-3.11.1Risk Assessments
Security Awareness Training
A.6.3Information security awareness, education and training
AT.L2-3.2.1Role-Based Risk Awareness
AT.L2-3.2.2Role-Based Training
Data Classification
A.5.12Classification of information
A.8.10Information deletion
A.8.12Data leakage prevention
MP.L2-3.8.1Media Protection
Configuration Management
A.8.9Configuration management
CM.L2-3.4.1System Baselining
CM.L2-3.4.2Security Configuration Enforcement
Malware Protection
A.8.7Protection against malware
SI.L2-3.14.2Malicious Code Protection

A row means the two requirements cover the same ground, so one implementation and one set of evidence can usually serve both. It does not mean satisfying one certifies the other: each framework keeps its own scope, wording and assessment, and some requirements have no counterpart at all. Treat this as a starting map for planning, then confirm each row against the requirement text.

Go deeper

Your CMMC reading list.

Visit the knowledge centre

Before you get started

A few useful answers.

Want to discuss your framework and current process?

Talk it through with us
Can any CMMC gap be deferred in a POA&M?

No. Eligibility, limits and closeout rules depend on the applicable CMMC requirements. Venvera can track the plan; your team must confirm whether a given item can be treated this way.

Is Venvera a CMMC assessor?

No. Venvera supports preparation and programme management. The required self-assessment or authorised assessment process is determined by your CMMC level and contract requirements.

Can we use our existing evidence?

Yes. Bring your policies and supporting evidence into Venvera and link them to the relevant controls. Cross-framework mappings help you identify reusable work; your team still reviews whether the evidence meets each requirement.

What is included in the trial?

The 14-day Professional trial includes up to five frameworks and unlimited users, with no credit card required. You can explore the controls, assess gaps and organise your compliance work. Framework modules are on paid plans; compare plans for feature availability.

CMMC by Venvera

Give your next review a clearer starting point.

14-day Professional trial · no credit card required · up to 5 frameworks · unlimited users