Skip to framework content
NEWVenvera speaks your language: the full platform, in English, German, Spanish, Bulgarian, Arabic and Chinese.See what’s new →

GDPR compliance software

Know where your data goes. Keep the proof together.

Manage processing records, DPIAs, data subject requests and breach work in one GDPR workspace. Give privacy teams a clearer way to keep records current.

14-day Professional trial · no credit card required

Inside VenveraProduct preview
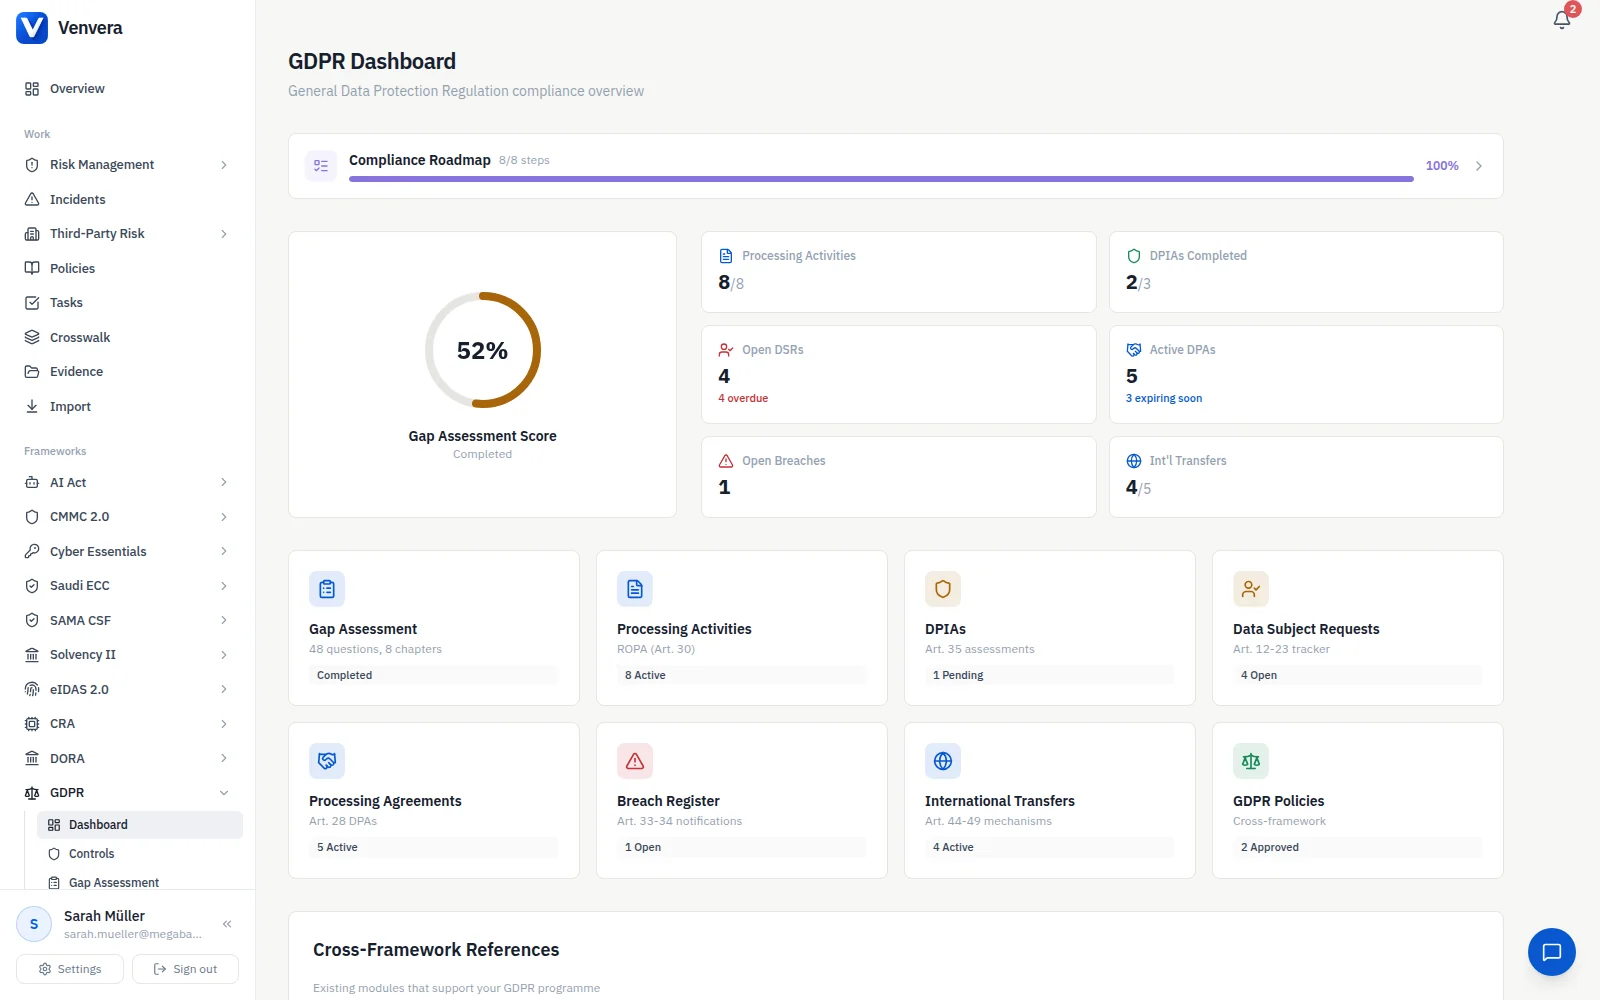
GDPR workspace: processing, assessments and privacy work in one view.
Real product screen · example dataExplore the workflow

A practical way to move forward

Know the work. See the progress.

One workspace for the requirements, the people doing the work and the records behind your next review.

Processing records

Make the data map useful.

Maintain records of processing activities and connect them to your wider privacy work. Bring processor agreements and transfer records into the same workspace.

  • Processing activity register
  • DPA and international transfer records
Privacy assessments

Give high-risk work a review trail.

Record DPIAs and assess gaps in your privacy programme. Keep your rationale and the work still to do accessible to the team responsible for it.

  • DPIA records and follow-up
  • GDPR control and gap assessment
Requests & breaches

Keep live cases moving.

Track data subject requests and personal data breach records alongside the programme. Give each case a shared place for its status and supporting information.

  • Data subject request tracking
  • Breach records and case detail

The detail behind the dashboard

Give every review a better starting point.

Move from a progress summary to the records that support it. Keep the next conversation focused on the work that needs attention.

Screens show example data. Shared platform features and availability depend on your plan.

See it with our team
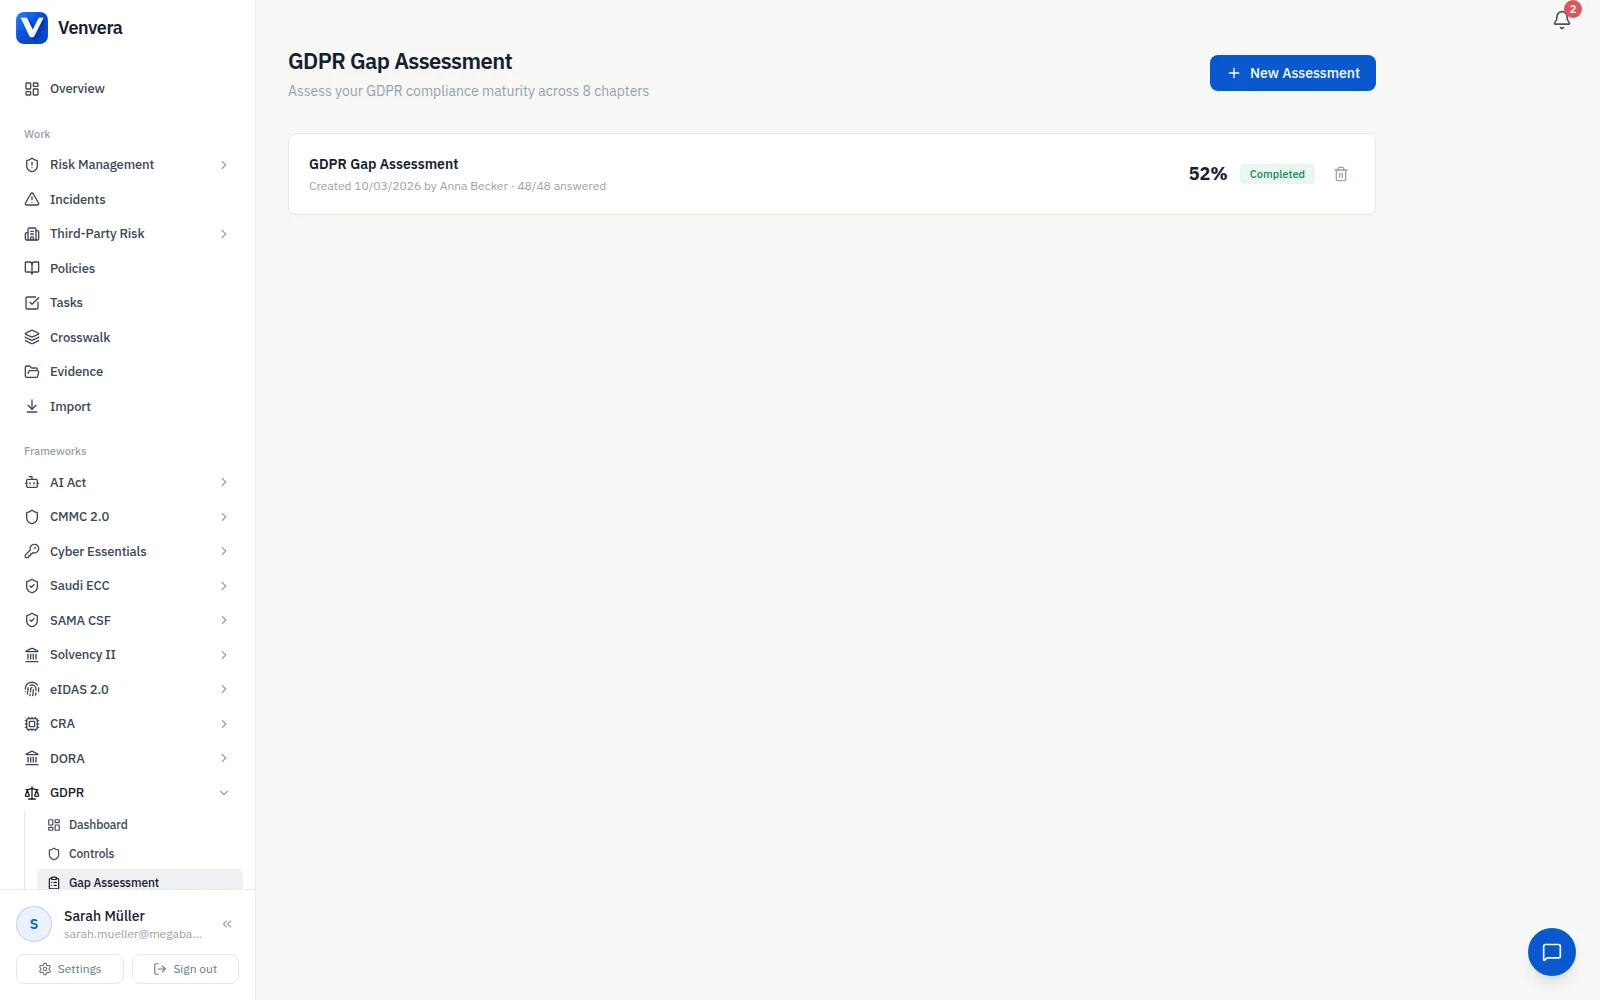
GDPR gap assessment: review the areas that need follow-up.
GDPR gap assessment: review the areas that need follow-up.Open full size

Start with the right scope

For privacy teams and DPOs coordinating data protection work.

GDPR responsibilities depend on your processing activities and your role as controller or processor. Some organisations outside the EU also fall within scope. Establish the applicable obligations for each activity.

European Commission: application of GDPR (opens in a new tab)

Use the work you already have

Find the overlap. Review the gaps.

Explore shared requirements and download a CSV. A mapping identifies related work; it does not certify compliance.

Explore GDPR control mappings
You already run
You have been asked to add
11 of the 53 domains in this crosswalk appear in both NIST SP 800-53 and GDPR.
DomainNIST SP 800-53GDPR
Encryption
SC-13Cryptographic Protection
SC-28Protection of Information at Rest
SC-8Transmission Confidentiality and Integrity
Art. 32(1)(a)Are pseudonymisation and encryption of personal data used where appropriate?
Key Management
SC-12Cryptographic Key Establishment and Management
Art. 32(1)(a)Are pseudonymisation and encryption of personal data used where appropriate?
Access Control
AC-3Access Enforcement
AC-6Least Privilege
Art. 32(4)Are persons authorised to process personal data committed to confidentiality or under an appropriate statutory obligation?
Incident Management
IR-4Incident Handling
Art. 33(1)Does the organization have a process to detect, report and investigate personal data breaches?
Incident Reporting
IR-6Incident Reporting
Art. 33(1)Can the organization notify the supervisory authority of a personal data breach within 72 hours of becoming aware of it?
Business Continuity
CP-2Contingency Plan
Art. 32(1)(c)Does the organization have the ability to restore the availability and access to personal data in a timely manner in the event of an incident?
Supplier Contracts
SR-5Acquisition Strategies, Tools, and Methods
PS-7External Personnel Security
Art. 28Are written contracts or legal acts in place with all data processors, containing the mandatory Article 28 provisions?
Data Classification
MP-4Media Storage
Art. 5(1)(c)Is personal data adequate, relevant and limited to what is necessary in relation to the purposes for which it is processed?
Security Testing
SA-11Developer Testing and Evaluation
CA-2Control Assessments
Art. 32(1)(d)Is there a process for regularly testing, assessing and evaluating the effectiveness of technical and organisational security measures?
Breach Notification
IR-6Incident Reporting
SR-8Notification Agreements
Art. 33(1)Can the organization notify the supervisory authority of a personal data breach within 72 hours of becoming aware of it?
Art. 34(1)Does the organization have a process to communicate a breach to affected data subjects without undue delay when there is a high risk to their rights and freedoms?
Data Protection Impact Assessment
RA-8Privacy Impact Assessments
Art. 35(1)Does the organization carry out a DPIA where a type of processing is likely to result in a high risk to the rights and freedoms of natural persons?

A row means the two requirements cover the same ground, so one implementation and one set of evidence can usually serve both. It does not mean satisfying one certifies the other: each framework keeps its own scope, wording and assessment, and some requirements have no counterpart at all. Treat this as a starting map for planning, then confirm each row against the requirement text.

Go deeper

Your GDPR reading list.

Visit the knowledge centre

Before you get started

A few useful answers.

Want to discuss your framework and current process?

Talk it through with us
Can controllers and processors use the workspace?

Yes. Both can use Venvera to organise their data protection work. The records and obligations you need depend on your role and processing activities.

Does software make our organisation GDPR compliant?

Compliance depends on your processing decisions, safeguards and day-to-day practices. Venvera helps you maintain the records and manage the work; your organisation remains responsible for its obligations.

Can we use our existing evidence?

Yes. Bring your policies and supporting evidence into Venvera and link them to the relevant controls. Cross-framework mappings help you identify reusable work; your team still reviews whether the evidence meets each requirement.

What is included in the trial?

The 14-day Professional trial includes up to five frameworks and unlimited users, with no credit card required. You can explore the controls, assess gaps and organise your compliance work. Framework modules are on paid plans; compare plans for feature availability.

GDPR by Venvera

Give your next review a clearer starting point.

14-day Professional trial · no credit card required · up to 5 frameworks · unlimited users