Start with what you need to protect.
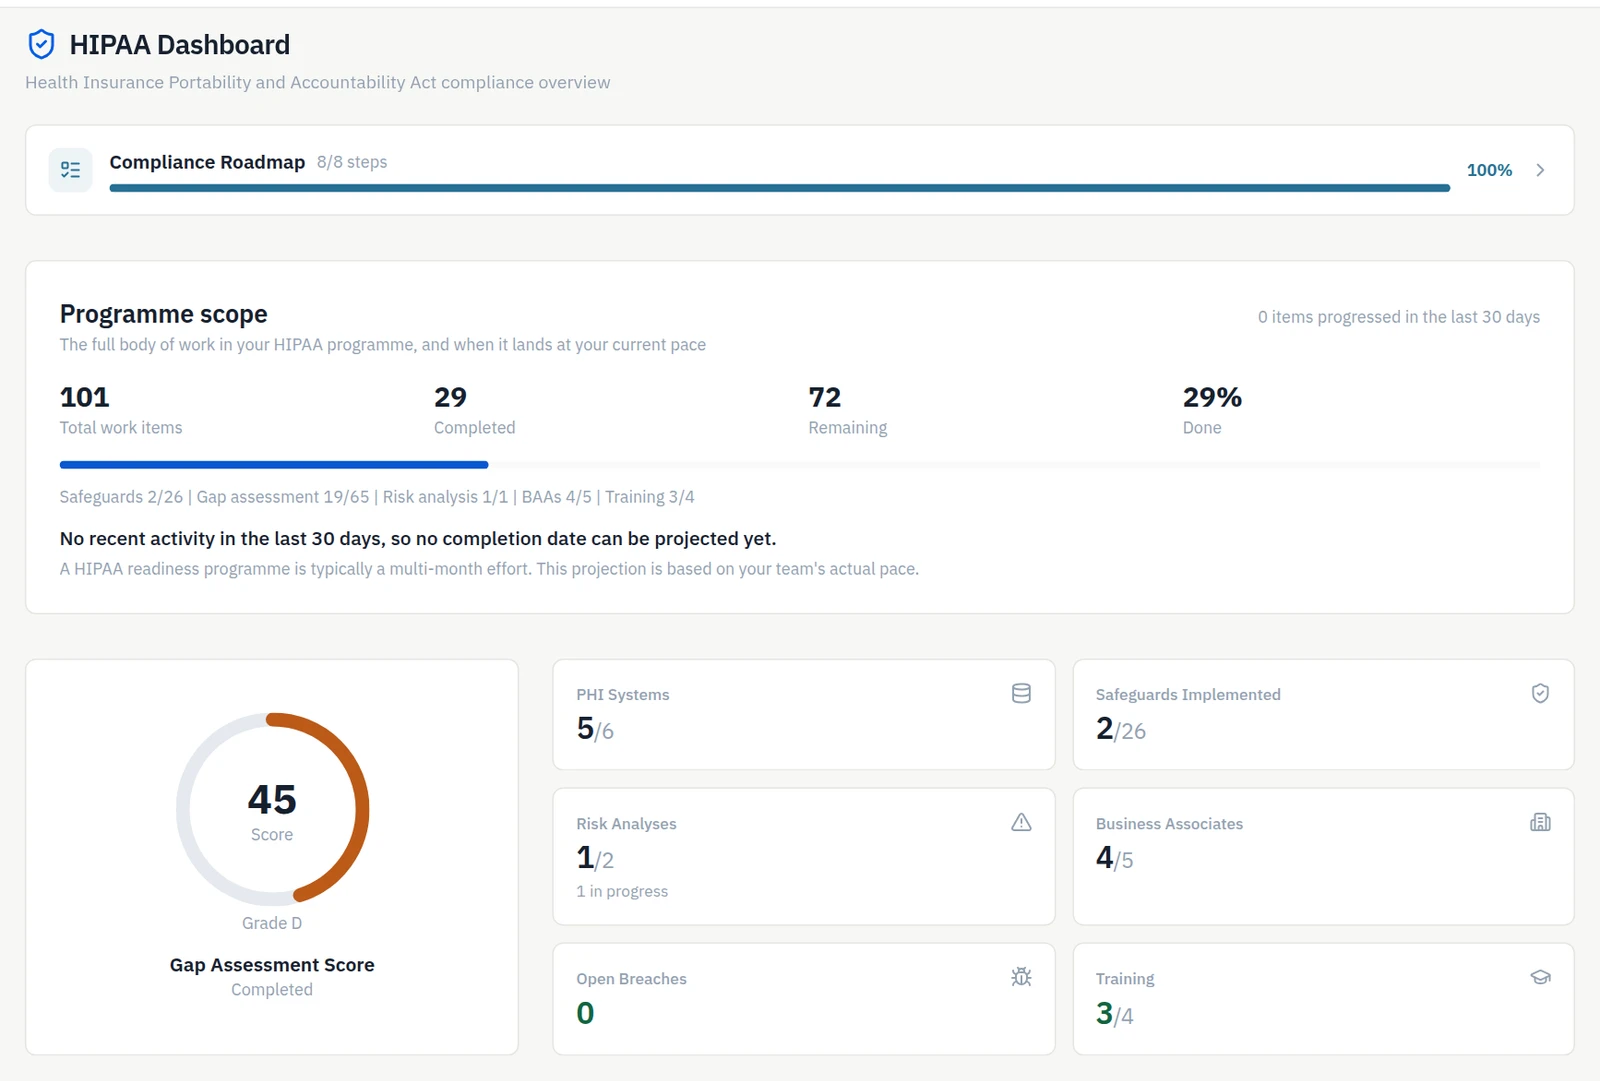
Maintain a PHI inventory and review safeguards. Connect the records to policies and controls so your team can see the work behind the status.
- PHI inventory and safeguards
- Policy and control records
HIPAA compliance software
Coordinate HIPAA safeguards, risk analyses, business associates and breach records. Give the team a shared place to manage work around protected health information.
14-day Professional trial · no credit card required
A practical way to move forward
One workspace for the requirements, the people doing the work and the records behind your next review.
Maintain a PHI inventory and review safeguards. Connect the records to policies and controls so your team can see the work behind the status.
Record risk analyses and assess gaps in your programme. Keep open issues available for follow-up as your systems and operations change.
Track business associates, training and breach records in the same workspace. Bring the people and third-party work into your programme reviews.
The detail behind the dashboard
Move from a progress summary to the records that support it. Keep the next conversation focused on the work that needs attention.
Screens show example data. Shared platform features and availability depend on your plan.
See it with our team
Start with the right scope
HIPAA applies to covered entities and business associates as defined by the rules. The Security Rule addresses electronic protected health information; privacy and breach-notification duties require related, distinct work.
HHS: HIPAA Security Rule (opens in a new tab)Use the work you already have
Explore shared requirements and download a CSV. A mapping identifies related work; it does not certify compliance.
A row means the two requirements cover the same ground, so one implementation and one set of evidence can usually serve both. It does not mean satisfying one certifies the other: each framework keeps its own scope, wording and assessment, and some requirements have no counterpart at all. Treat this as a starting map for planning, then confirm each row against the requirement text.
The four penalty tiers at the 2026 amounts, the yearly caps OCR applies, and how a missing control is counted by the day.
The two Required duties under 164.308(a)(1), the elements OCR expects, and a scored example.
Whether HIPAA reaches you, and which business associate agreements that requires.
Before you get started
Want to discuss your framework and current process?
Talk it through with usNo. Venvera is a workspace for managing safeguards and compliance records. Using it does not confer government certification or establish that your organisation meets every HIPAA obligation.
Yes. Business associates can organise their own HIPAA work in the module. Confirm the obligations that apply to your services and business associate agreements, including your handling of electronic protected health information.
Yes. Bring your policies and supporting evidence into Venvera and link them to the relevant controls. Cross-framework mappings help you identify reusable work; your team still reviews whether the evidence meets each requirement.
The 14-day Professional trial includes up to five frameworks and unlimited users, with no credit card required. You can explore the controls, assess gaps and organise your compliance work. Framework modules are on paid plans; compare plans for feature availability.
HIPAA by Venvera
14-day Professional trial · no credit card required · up to 5 frameworks · unlimited users