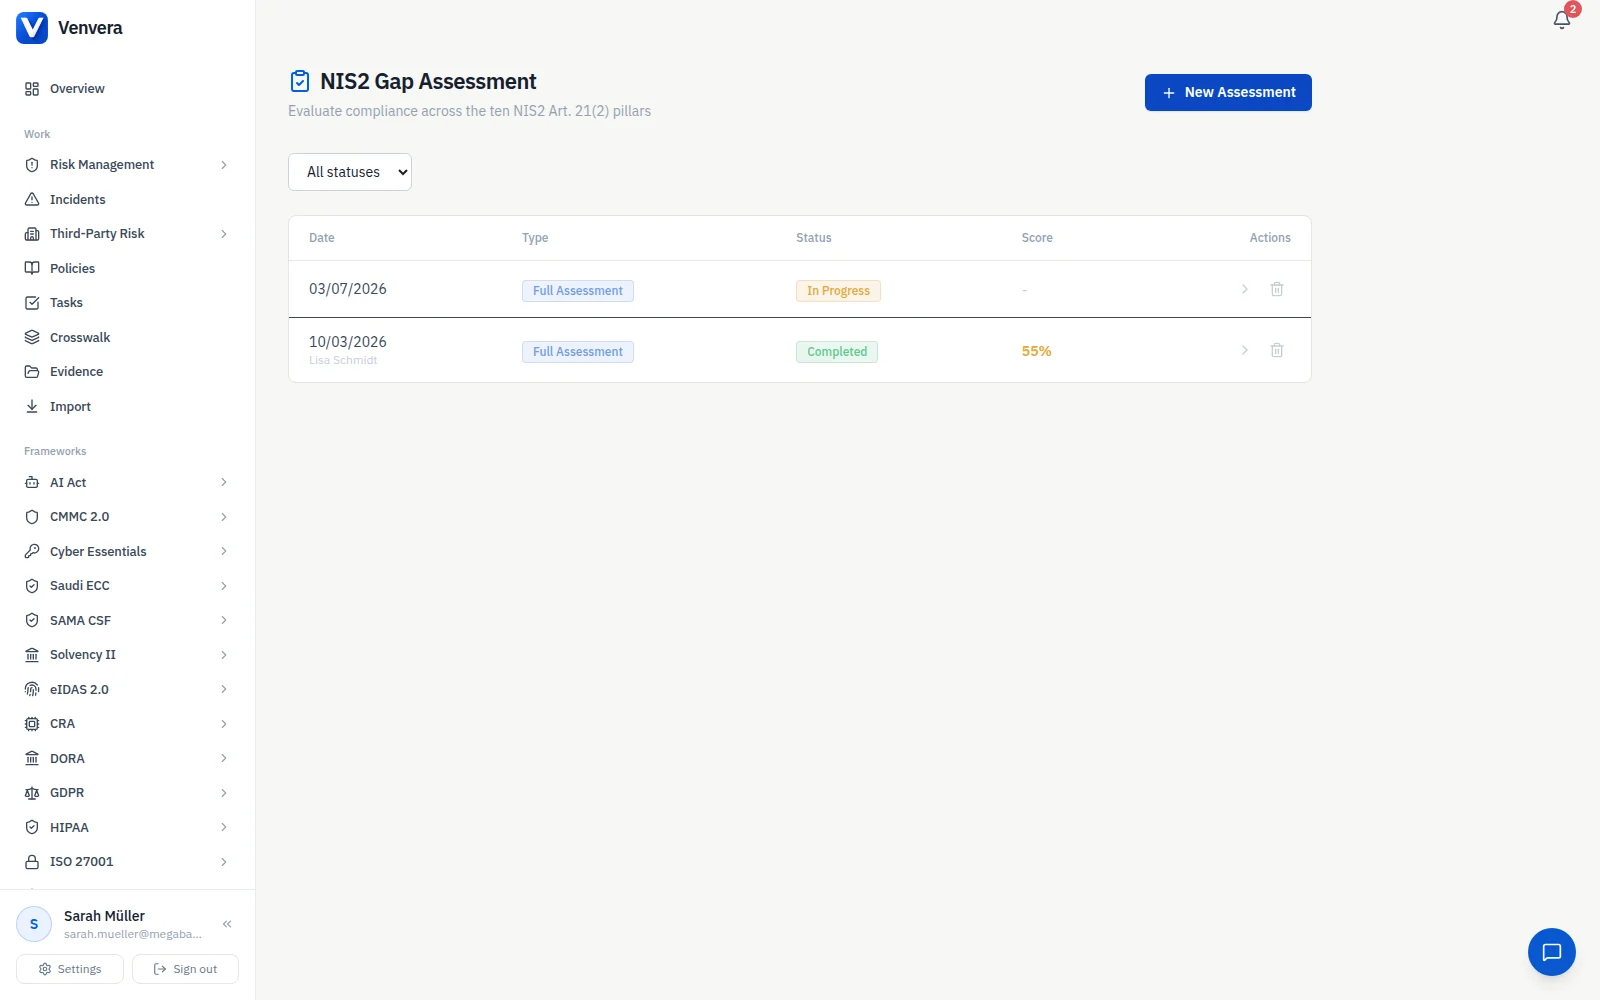
| Encryption | SC-13Cryptographic Protection SC-28Protection of Information at Rest SC-8Transmission Confidentiality and Integrity | Art. 21(2)(h)Are policies and procedures in place governing the use of cryptography, including encryption standards for data at rest and in transit? |
| Key Management | SC-12Cryptographic Key Establishment and Management | Art. 21(2)(h)Are cryptographic key management procedures documented, covering key generation, distribution, storage, rotation, and destruction? |
| Access Control | AC-3Access Enforcement AC-6Least Privilege | Art. 21(2)(i)Is there a formal access control policy enforcing least privilege principle, with documented procedures for access provisioning and de-provisioning? |
| Identity Management | AC-2Account Management IA-4Identifier Management | Art. 21(2)(i)Is there a formal access control policy enforcing least privilege principle, with documented procedures for access provisioning and de-provisioning? |
| Authentication & MFA | IA-2Identification and Authentication (Organizational Users) IA-5Authenticator Management | Art. 21(2)(j)Is multi-factor authentication or continuous authentication deployed for access to critical systems, remote access, and privileged accounts? |
| Access Rights Review | | Art. 21(2)(i)Are access rights reviewed regularly (at least annually) and recertified, with privileged access subject to enhanced controls and monitoring? |
| Privileged Access Management | AC-6Least Privilege AC-5Separation of Duties | Art. 21(2)(i)Are access rights reviewed regularly (at least annually) and recertified, with privileged access subject to enhanced controls and monitoring? |
| Network Security | SC-7Boundary Protection AC-17Remote Access | Art. 21(2)(g)Are basic cyber hygiene practices established and enforced, including patching, password policies, device management, and network segmentation? |
| Vulnerability Management | RA-5Vulnerability Monitoring and Scanning SI-2Flaw Remediation | Art. 21(2)(e)Is there a vulnerability handling and disclosure process that ensures timely identification, assessment, and remediation of vulnerabilities? |
| Logging & Monitoring | AU-2Event Logging AU-6Audit Record Review, Analysis, and Reporting AU-12Audit Record Generation SI-4System Monitoring | Art. 21(2)(f)Are security metrics and KPIs defined, tracked, and reported to management to measure the effectiveness of cybersecurity controls? |
| Incident Management | | Art. 21(2)(b)Is there a documented incident handling procedure covering detection, analysis, containment, eradication, and recovery phases? |
| Incident Classification | | Art. 23(3)Are incident classification criteria documented, distinguishing significant incidents based on impact on service provision, affected users, duration, and geographic scope? |
| Incident Reporting | | Art. 23(4)(a)–(b)Can your organisation submit an early warning to the CSIRT within 24 hours and an incident notification within 72 hours of becoming aware of a significant incident? |
| Incident Response Team | IR-8Incident Response Plan | Art. 21(2)(b)Is there a documented incident handling procedure covering detection, analysis, containment, eradication, and recovery phases? |
| Post-Incident Review | | Art. 21(2)(b)Do you perform post-incident reviews for significant incidents, with root cause analysis and lessons learned fed into risk management improvements? |
| Business Continuity | | Art. 21(2)(c)Are business continuity and disaster recovery plans documented, covering all critical services, with defined RTO/RPO targets and tested at least annually? |
| Backup & Restoration | CP-9System Backup CP-10System Recovery and Reconstitution | Art. 21(2)(c)Are backup procedures implemented with defined scope, frequency, and secure off-site storage, with regular restoration testing? |
| Crisis Management | CP-4Contingency Plan Testing | Art. 21(2)(c)Is there a crisis management framework with defined escalation procedures, communication plans, and designated crisis management team? |
| Third-Party Risk Management | SR-2Supply Chain Risk Management Plan | Art. 21(2)(d)Is there a documented supply chain security policy covering ICT product and service procurement, with security requirements for suppliers? |
| Supplier Due Diligence | SR-6Supplier Assessments and Reviews SA-4Acquisition Process | Art. 21(2)(d)Do you assess the cybersecurity posture and practices of direct suppliers and service providers before entering into agreements? |
| Supplier Contracts | SR-5Acquisition Strategies, Tools, and Methods PS-7External Personnel Security | Art. 21(2)(d)Do supplier contracts include cybersecurity requirements, incident notification obligations, and audit/assessment rights? |
| Supplier Monitoring | SR-3Supply Chain Controls and Processes SR-6Supplier Assessments and Reviews | Art. 21(2)(d)Are supply chain risks and supplier cybersecurity performance monitored on an ongoing basis, with periodic re-assessment? |
| Risk Assessment | RA-3Risk Assessment PM-9Risk Management Strategy | Art. 21(2)(a)Is there a formal, documented risk analysis methodology that identifies and assesses cybersecurity risks to network and information systems? |
| Information Security Policy | AC-1Policy and Procedures PL-2System Security and Privacy Plans | Art. 21(2)(a)Has the management body approved a comprehensive information security policy covering all network and information systems, reviewed at least annually? |
| Security Awareness Training | AT-2Literacy Training and Awareness AT-3Role-Based Training | Art. 20(2), Art. 21(2)(g)Is there a cybersecurity awareness and training programme for all staff, including management body members, with regular refresher sessions? |
| Change Management | CM-3Configuration Change Control | Art. 21(2)(e)Is there a formal change management process for network and information systems that includes security impact assessment and testing? |
| Secure Development | SA-3System Development Life Cycle SA-8Security and Privacy Engineering Principles | Art. 21(2)(e)Are secure development practices (secure coding guidelines, code review, security testing) applied to in-house and custom-developed software? |
| Security Testing | SA-11Developer Testing and Evaluation CA-2Control Assessments | Art. 21(2)(f)Are there defined policies and procedures to assess the effectiveness of cybersecurity risk-management measures, including regular security testing? |
| Penetration Testing | | Art. 21(2)(f)Are there defined policies and procedures to assess the effectiveness of cybersecurity risk-management measures, including regular security testing? |
| Breach Notification | IR-6Incident Reporting SR-8Notification Agreements | Art. 23(4)(a)–(b)Can your organisation submit an early warning to the CSIRT within 24 hours and an incident notification within 72 hours of becoming aware of a significant incident? |