NEWVenvera speaks your language: the full platform, in English, German, Spanish, Bulgarian, Arabic and Chinese.See what’s new →
Alexander Sverdlov
Author

Alexander Sverdlov

CEO and founder, Venvera

Alexander is the founder of Venvera and a 20+ year veteran of European cybersecurity and compliance. He has led security and risk programmes for regulated financial institutions, fintechs and SaaS companies operating under DORA, NIS2, GDPR, ISO 27001 and the EU AI Act. Before Venvera, he founded Atlant Security, an offensive security consultancy that ran penetration tests, red-team exercises and ISO 27001 readiness programmes for clients across the EU and the Middle East. He writes on the cross-framework realities of running modern compliance: how to map one control to many obligations, where the spreadsheets fall apart, and what regulators are actually asking for once the auditor sits down.

Expertise

  • DORA implementation and Register of Information
  • NIS2 readiness and supply-chain risk
  • ISO 27001 / 27002 implementation and audit prep
  • GDPR and DPO operations
  • EU AI Act conformity assessment
  • Cross-framework control mapping and crosswalking
  • Operational resilience testing (TLPT, scenario testing)
  • Third-party risk management and vendor due diligence
  • Offensive security and red-team operations
  • Board-level reporting on compliance posture

Background

  • Founder and CEO, Venvera - GRC compliance platform
  • Founder, Atlant Security - offensive security and ISO 27001 consultancy
  • 20+ years in cybersecurity, compliance and risk management
  • Hands-on author of 125+ field-tested articles on DORA, NIS2, GDPR and ISO 27001
  • Built compliance programmes for regulated entities across the EU, UAE and Saudi Arabia
Find me:linkedin.com/in/alexsverdlatlantsecurity.com

Articles by Alexander (202)

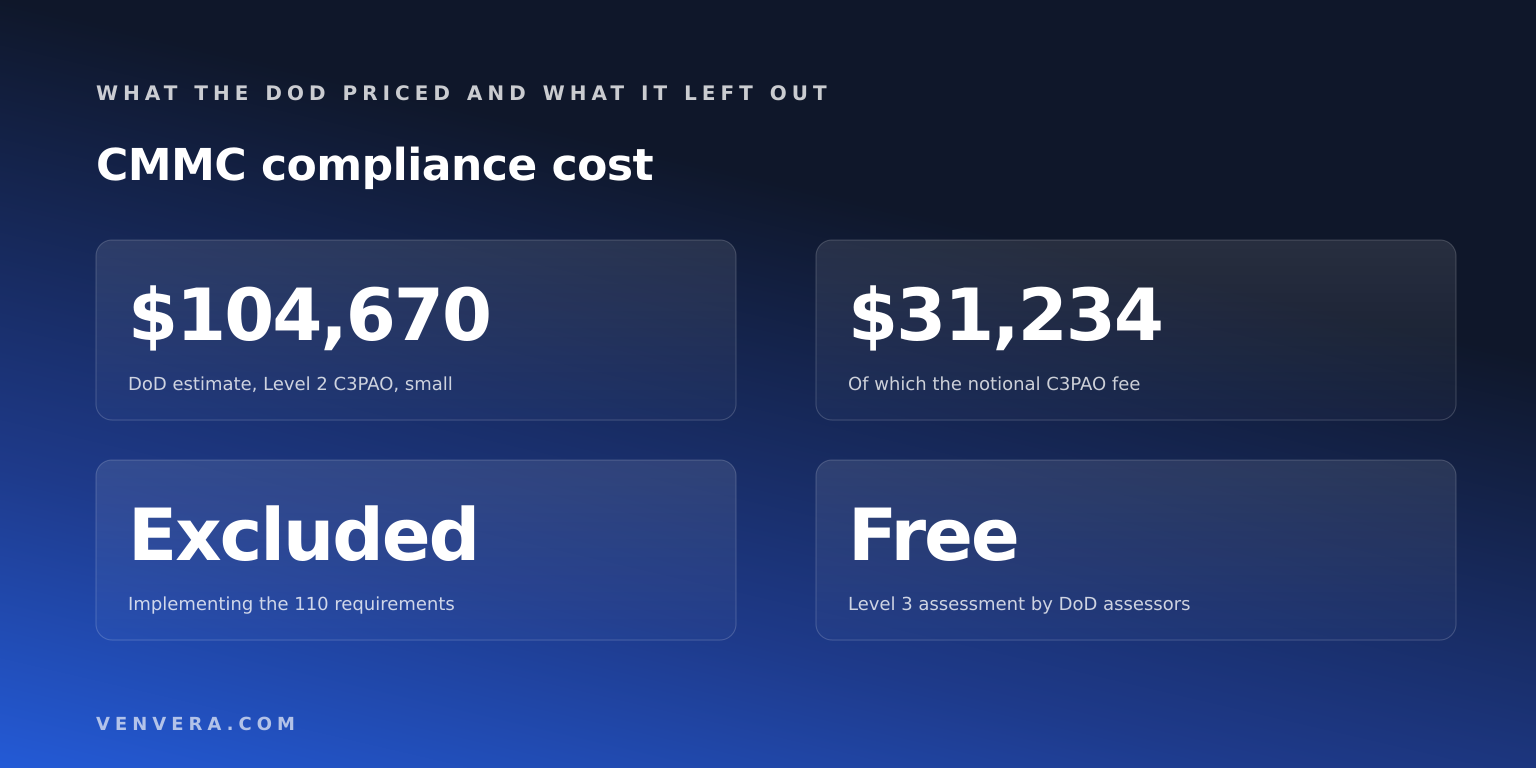
CMMC Compliance Cost: What the DoD Estimated
Learn

CMMC Compliance Cost: What the DoD Estimated

The DoD puts a small firm's Level 2 C3PAO route at $104,670 over three years, but that figure leaves out the controls. What it covers and what you must add.

UAE IA vs ISO 27001: Where They Differ
Learn

UAE IA vs ISO 27001: Where They Differ

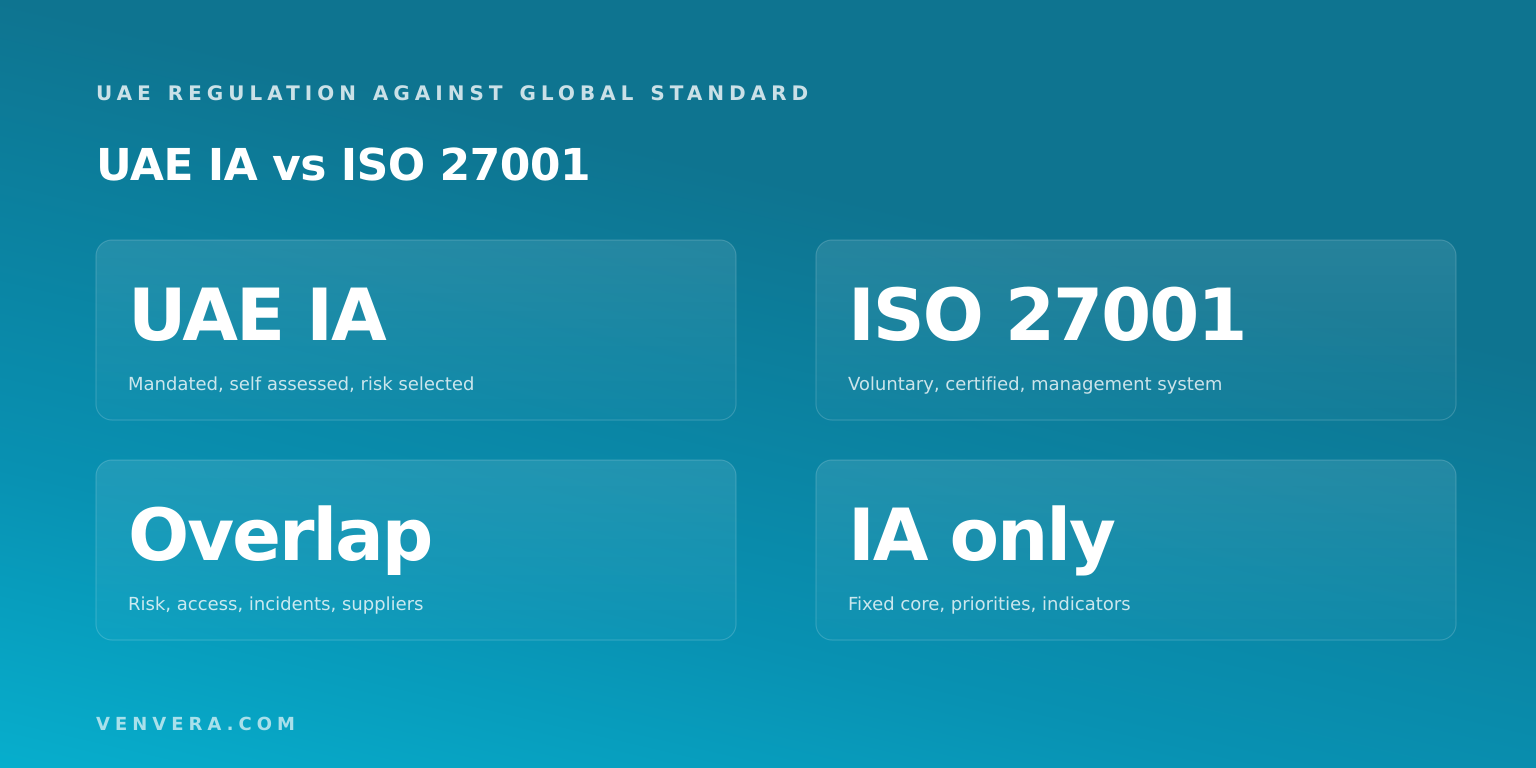
An ISO 27001 certificate builds much of a UAE IA programme but stands in for none of it. The overlap, the IA only rules, and which edition you are held to.

Saudi NCA ECC vs SAMA CSF: Scope and Differences
Learn

Saudi NCA ECC vs SAMA CSF: Scope and Differences

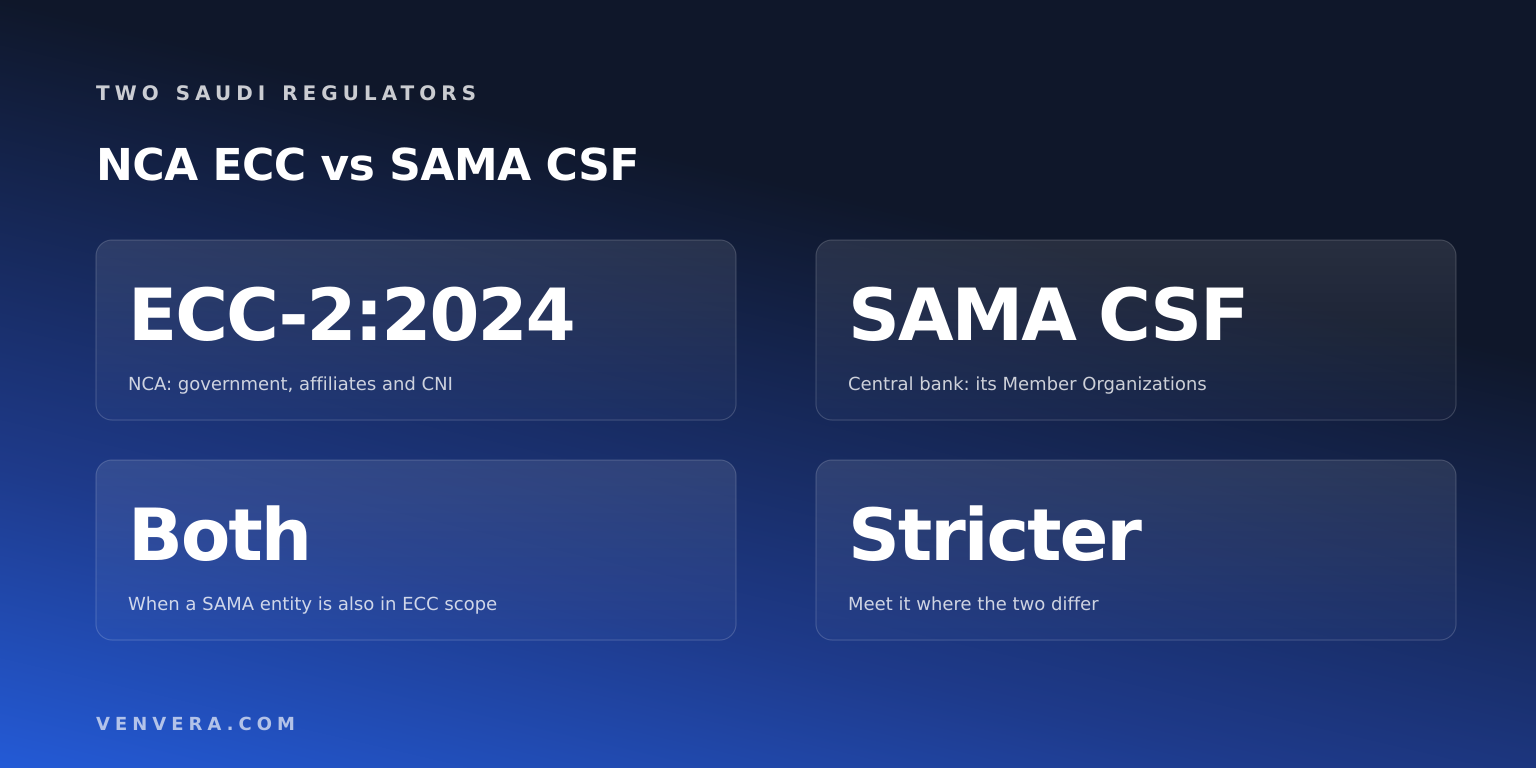
Who the NCA's ECC-2:2024 and the SAMA CSF each bind, when a financial institution answers to both, and the rules where the two disagree. From the texts.

SAMA CSF vs ISO 27001: What a Certificate Covers
Learn

SAMA CSF vs ISO 27001: What a Certificate Covers

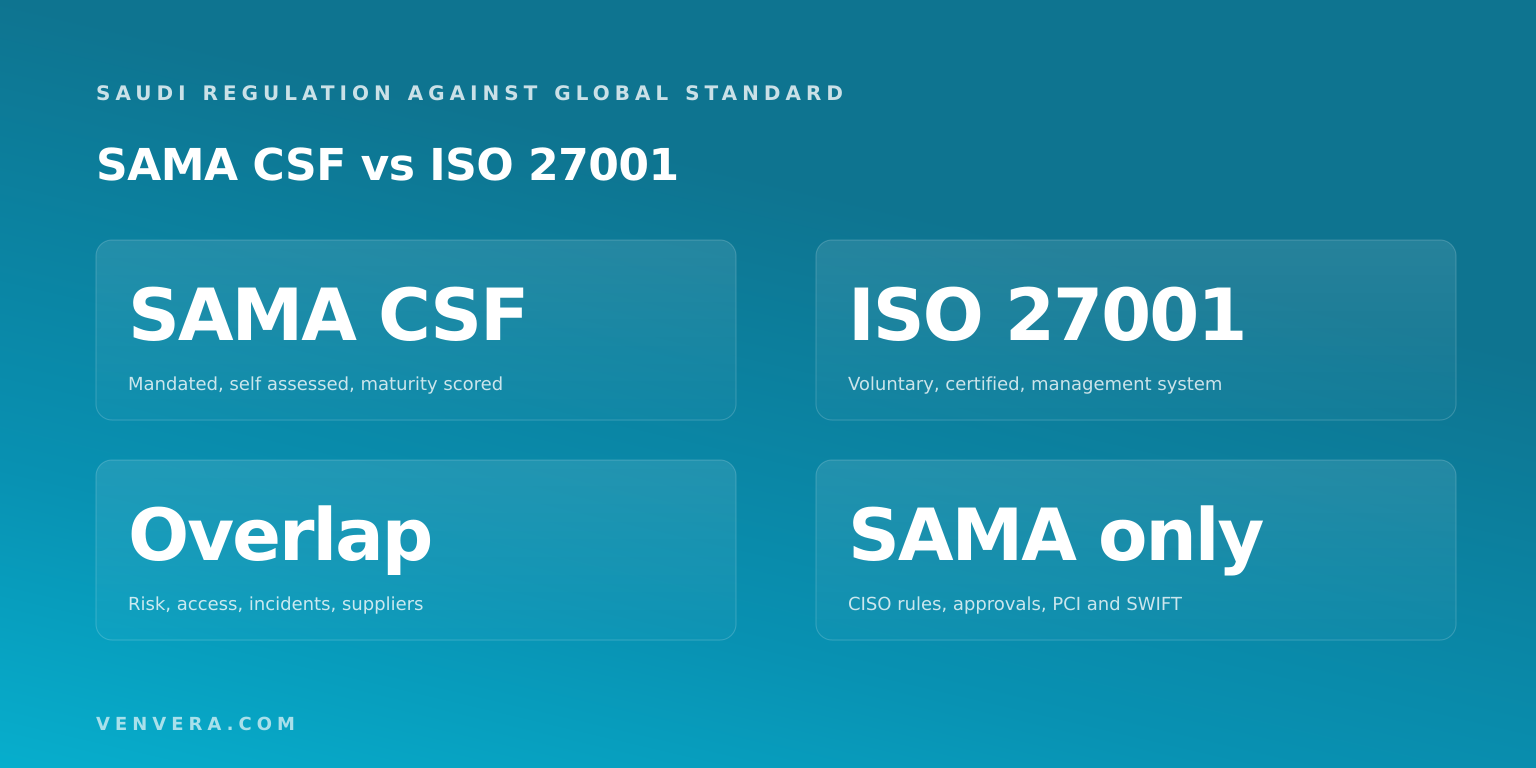
An ISO 27001 certificate builds much of a SAMA CSF programme but replaces none of it. Where the two overlap, and the SAMA rules the standard never asks for.

GDPR vs NDPA: Where Nigeria's Law Differs
Learn

GDPR vs NDPA: Where Nigeria's Law Differs

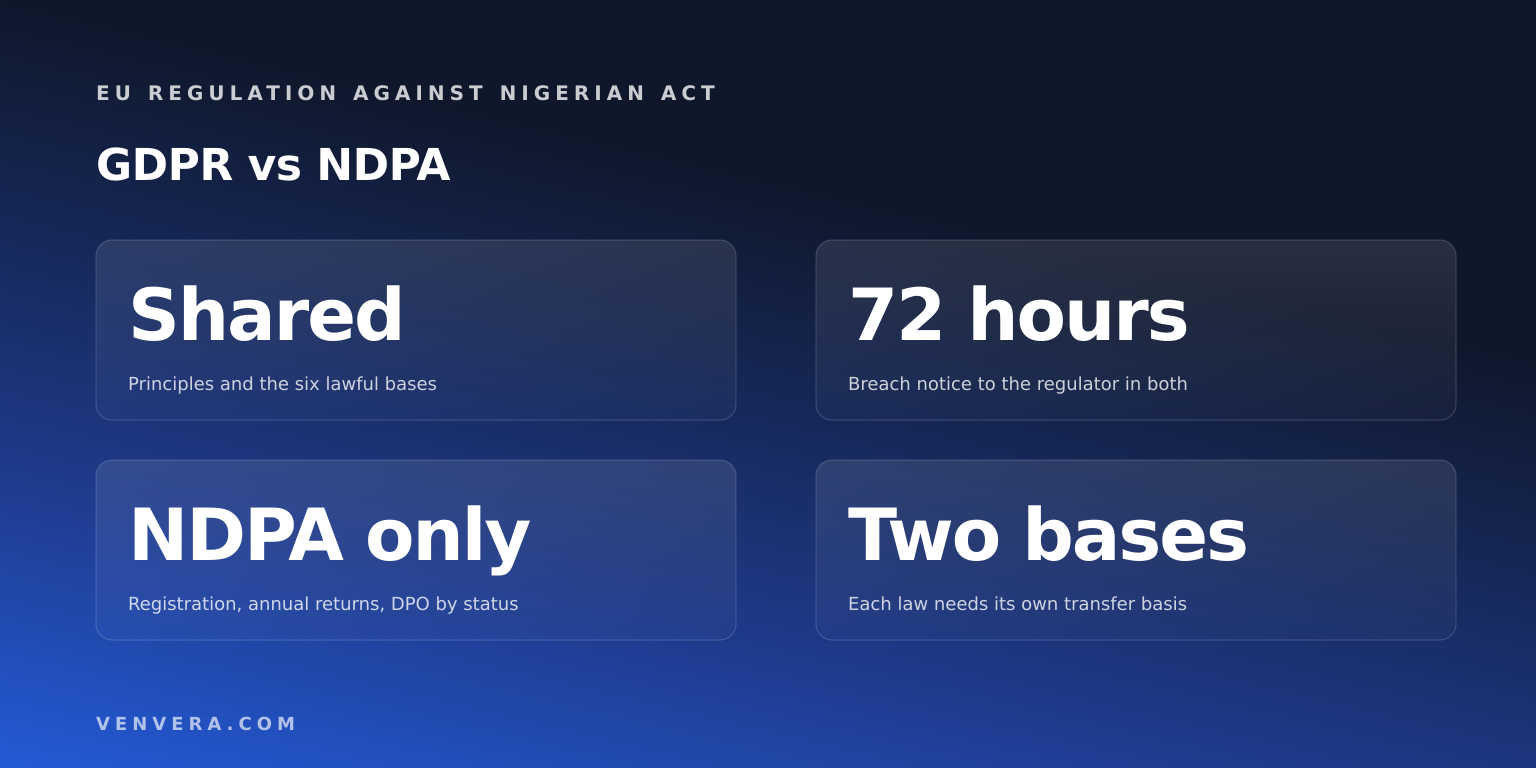
The NDPA borrows GDPR's principles and six lawful bases, then parts ways on registration, annual returns, breach notice, fines and transfers. Side by side.

SOC 2 vs ISO 27001: What EU Buyers Ask For
Learn

SOC 2 vs ISO 27001: What EU Buyers Ask For

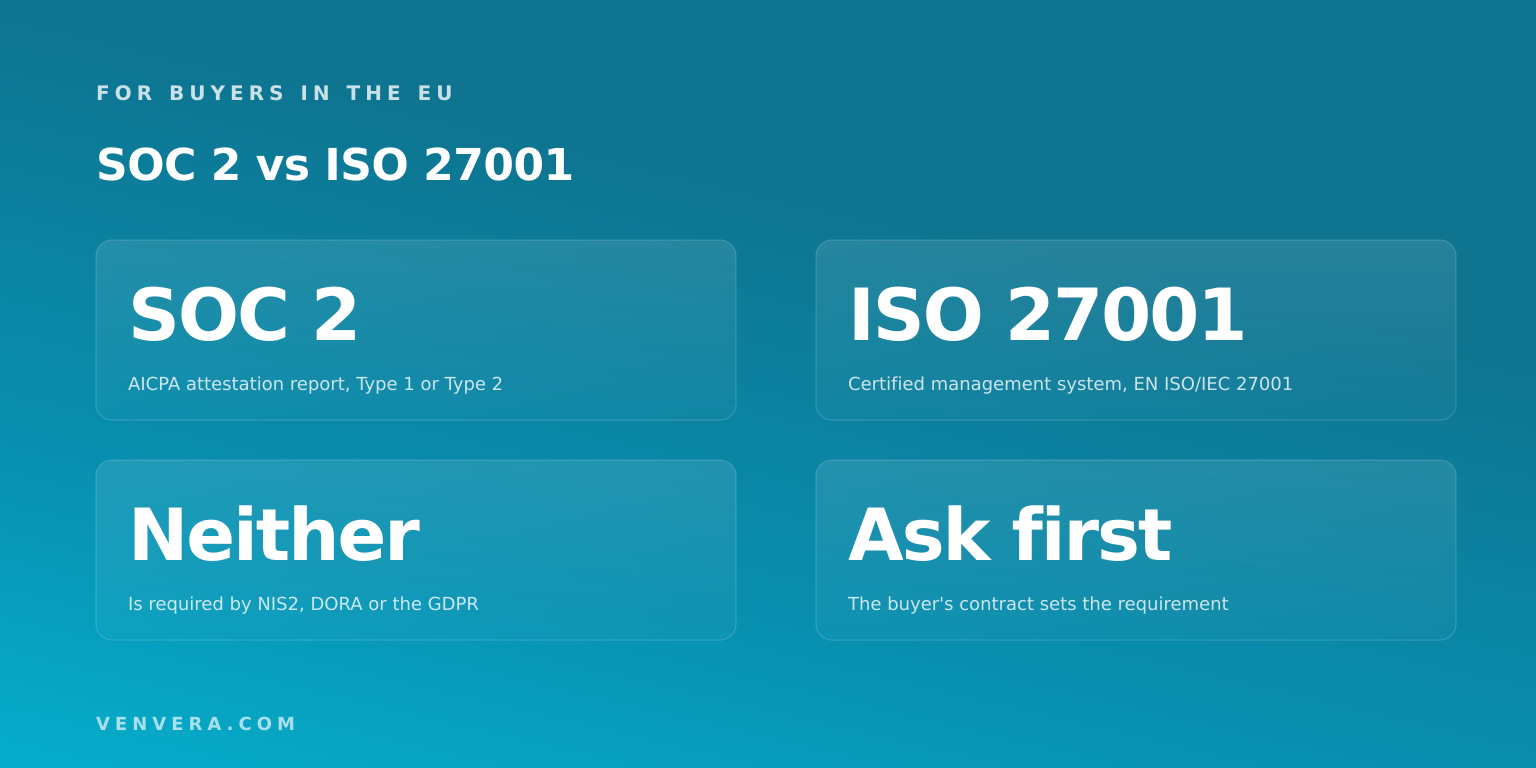
NIS2, DORA and the GDPR require neither. What those laws and German C5 say about each, and how to pick the one an EU customer's procurement team will accept.

PCI DSS vs ISO 27001: Scope, Proof and Overlap
Learn

PCI DSS vs ISO 27001: Scope, Proof and Overlap

PCI DSS protects card data under rules the brands enforce; ISO 27001 certifies a system you scope. Where they overlap, and why neither replaces the other.

ISO 27001 vs DORA: What the Certificate Covers
Learn

ISO 27001 vs DORA: What the Certificate Covers

DORA never mentions ISO 27001. Where an ISMS already answers its ICT risk articles, and the reporting, register, contract and testing duties it leaves open.

SOC 2 Audit: What to Expect From Start to Report
Learn

SOC 2 Audit: What to Expect From Start to Report

What happens in a SOC 2 examination: the description and assertion you write, how a Type 2 is tested, vendors, the four possible opinions, the final letter.

HIPAA Fines and Penalties: What OCR Really Charges
Learn

HIPAA Fines and Penalties: What OCR Really Charges

HIPAA penalty tiers at the amounts in force since January 2026, the 2019 yearly caps OCR still applies, how one gap becomes a daily violation, real cases.

PCI DSS Compliance Cost: What Drives the Bill
Learn

PCI DSS Compliance Cost: What Drives the Bill

Nobody publishes a PCI DSS price. What sets yours: the validation route your card brand and acquirer require, the tests the standard mandates, and your scope.

ISO 27001 Audit: What to Expect in the Room
Learn

ISO 27001 Audit: What to Expect in the Room

What happens inside an ISO 27001 certification audit: the opening meeting, sampling and interviews, major and minor findings, the closing meeting, the report.

How Long Does ISO 27001 Certification Take?
Learn

How Long Does ISO 27001 Certification Take?

No standard sets a duration. What has to exist before stage 1, what happens between the two audit stages, and what can hold the certificate back.

GDPR Fines and Penalties: What Changed in 2026
Learn

GDPR Fines and Penalties: What Changed in 2026

The two GDPR fine tiers, whose turnover counts, why fault is now required, how the EDPB sets the amount, and the fines and rule changes of 2026.

SOC 2 Cost for Companies Outside the US
Learn

SOC 2 Cost for Companies Outside the US

What sets a SOC 2 fee when you are not a US company: who may sign the report, AICPA versus ISAE 3000, report type, the period and the scope.

ISO 27001 Certification Cost: What Sets the Price
Learn

ISO 27001 Certification Cost: What Sets the Price

There is no ISO price list. How audit days follow headcount, what the three year cycle bills you for, and what accreditation in Europe changes.

NIS2 for Healthcare Providers: Scope and Duties
Learn

NIS2 for Healthcare Providers: Scope and Duties

Which hospitals, clinics and pharmacies NIS2 covers, why a public hospital is sized like any other, and what Articles 20, 21 and 23 ask of them.

DORA for Payment Institutions: Scope and TLPT
Learn

DORA for Payment Institutions: Scope and TLPT

Which payment and e-money institutions DORA covers, what it changed in PSD2 incident reporting, and when a payment firm must run TLPT.

NIS2 for Manufacturers: Scope and Obligations
Learn

NIS2 for Manufacturers: Scope and Obligations

Which manufacturers NIS2 covers, why most are important rather than essential entities, and what Articles 20, 21 and 23 ask of a plant operator.

DORA for Insurers: Scope, Solvency II and TLPT
Learn

DORA for Insurers: Scope, Solvency II and TLPT

Which insurers, reinsurers and intermediaries DORA covers, what it changed in Solvency II, and when an insurer must report an incident or run TLPT.

MiCA Requirements for CASPs Explained
Learn

MiCA Requirements for CASPs Explained

What MiCA Title V asks of a crypto-asset service provider: authorisation, capital, governance, client asset safekeeping and the service rules.

EU AI Act High-Risk Requirements Explained
Learn

EU AI Act High-Risk Requirements Explained

The seven requirements a high-risk AI system must meet under Articles 8 to 15, what providers and deployers each owe, and what the 2026 Omnibus changed.

UAE IA Audit: What to Expect
Learn

UAE IA Audit: What to Expect

How UAE IA compliance is checked: self-assessment reports via your sector regulator, audits and tests where TRA sees fit, and the evidence it reads.

eIDAS 2.0 Relying Party Requirements
Learn

eIDAS 2.0 Relying Party Requirements

What eIDAS 2.0 asks of a wallet relying party: register, request only registered data, identify yourself, validate, accept pseudonyms, keep other routes.

← All Venvera insights